By default, Netskope steers HTTP(S) traffic on ports 80 and 443 to the Netskope proxy. To steer HTTP(S) traffic on non-standard ports, an admin needs to add those ports to the Non-Standard Port Steering configuration as mentioned in Configure a Custom Port.
If your tenant has Cloud Firewall, traffic on ports that are not in the Non-Standard Port Steering configuration goes to Cloud Firewall instead. Within Cloud Firewall, HTTP Auto-Detect finds HTTP(S) traffic on non-standard ports and sends it to the Netskope proxy for full inspection, so admins don’t need to add each port manually.
Supported Access Methods
-
IPSec
-
GRE
-
Netskope Client
-
Explicit Proxy over Tunnel
-
Explicit Proxy over Client
Enable HTTP Auto Detect
To enable HTTP Auto Detect on the tenant:
-
Log into your Netskope tenant.
-
Go to Settings > Security Cloud Platform > Configuration.
-
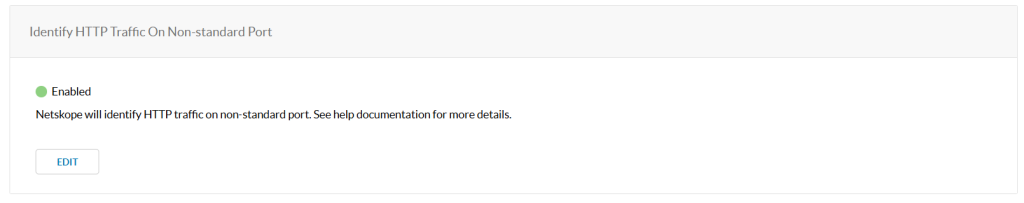
Go to Identify HTTP Traffic On Non-Standard Port and click Edit.
-
Select the toggle under Status to enable HTTP Auto detect.
Ports listed in your Non-Standard Port Steering configuration are not blocked. -
Click Save.