

After you’ve configured the interfaces on the DPoP, follow the instructions to configure the system and certificates.
Configure the System
First you need to install the tenant license key. You can get the license key from Settings > Security Cloud Platform next to where you downloaded the VA package.
- Copy the license key.
- In configuration mode, install the license key with the command:
set system licensekey <licensekey>. - Next, configure the system hostname. Set the hostname type with the command:
set system hostname <hostname>. - Set the primary and secondary DNS servers with the following commands:
set dns primary <DNS address>
set dns secondary <DNS address>
- Set the NTP server with the command:
set system ntp-servers <IP address or FQDN>.
Configure the Certificates
With connectivity now configured, you need to set up server side certificates to enable SSL inspection. You can use either a self-signed CA certificate or a CA certificate preferably signed by the enterprise’s Root or intermediate CA. See Use your own CA Certificates.
Alternatively, the DPoP can generate a self-signed certificate without CA. See Generate a Self-signed Certificate without CA.
Use your own CA Certificates
Make sure that the CA certificate of the DPoP has a common name.
- Enter the command:
set dataplane forward-proxy server-cert
Copy and paste your CA certificate in the buffer, press Enter, then type
Ctrl-Dto exit. - Enter the command:
set dataplane forward-proxy server-key
Copy and paste your private key in the buffer, press Enter, then type
Ctrl-Dto exit. - Enter the command:
set dataplane forward-proxy server-intermediate-ca-chain
Copy and paste any additional certificates in the following order:
- Server certificate (as provided in step 1)Intermediate CA certificate Root CA certificate
Press Enter, then type
Ctrl-Dto exit. - Enter
saveand press Enter to save the configuration.
Generate a Self-signed Certificate without CA
- If you are not using a CA and want the DPoP to generate a self-signed certificate, run the following command:
run request certificate generate forward-proxy self-signed city <city> common-name <common-name> country <country> days <days> email-address <email-address> organization <organization> organization-unit <organization-unit> state <state>
Here’s an example command to generate self-signed certificate:
run request certificate generate forward-proxy self-signed city "Los Altos" common-name "sforwarder.netskope.com" organization "netskope" organization-unit "netskope cert authority" state "CA" country "US" email-address "admin@netskope.com"
- Enter
saveand press Enter to save the configuration.
Enable the DPoP Connection
Now enable the DPoP
set dataplane forward-proxy enable true
Now save the entire configuration with the command save, and then press Enter.
You have now completed the installation and configuration of the DPoP, and DPoP will make an initial connection to Netskope cloud.
Note
From nsshell, you can use the SCP command to export and import a configuration.
Verify the DPoP Connection
To verify that DPoP successfully connected to tenant instance in the Netskope cloud, go to Settings > Security Cloud Platform > On-Premises Infrastructure. Scroll down the page until you see DPoP displayed with a Serial Number and Name. Last Seen shows the last time DPoP connected to the Netskope cloud.
Tip
It takes few minutes to refresh the status in the UI.
Verify the Certificates
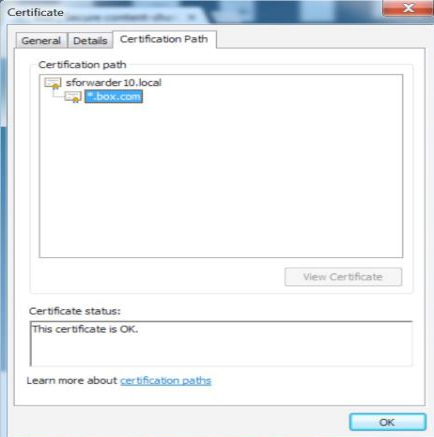
To verify that the cloud app traffic is forwarded by the DPoP to the tenant instance in the Netskope cloud, browse to any cloud app domain managed by Netskope (like Box.com) and verify that the SSL certificate presented is the certificate installed on the DPoP.
The image below shows a self-signed Root CA certificate installed on the DPoP that is presented to a browser.
 |