
Overview
Netskope DSPM supports scanning AWS MySQL Data Stores. Follow these instructions to set up your MySQL database and configure its connection to Netskope DSPM.
Authenticate Data Store
There are two methods for authenticating RDS and Aurora data stores: Snapshots or Service Account.
Using Snapshots
Snapshots are quicker and simpler, spinning up a secure copy of the data store for Netskope DSPM to scan without needing to create a Service Account. This copy exists only within your Netskope DSPM instance, and Netskope DSPM does not store any associated data. It’s encrypted and then immediately spun down, so there are no lingering data copies.
The following features are not supported when authenticating via Snapshot:
- Privilege Analysis
- Data-in-use monitoring
- Database selection
- Sample data collection
Ensure you’ve enabled Data Store Snapshots access during AWS Infrastructure onboarding. For already onboarded accounts, make sure the IAM policy used for DSPM includes the permissions required for Data Store Snapshots Access (note that this also requires the permissions from Feature 3: Unmanaged Data Stores). Depending on whether you onboarded an AWS Organization or an individual AWS account, you can find these granular permissions in the Onboard AWS Infrastructure Manually article under:
- Instructions > Onboard an AWS Organization > Step 3 (Optional): Create the Custom IAM Policy > Feature 4: Authorize Data Store Snapshots Access
- Instructions > Onboard an Individual AWS Account > Step 3 (Optional): Create the Custom IAM Policy > Feature 4: Authorize Data Store Snapshots Access
Once connected, data classification in the data store runs via Snapshot, which appears on the Data Store Inventory page as a small layered square note icon to the right of the hyperlinked data store name. You can later edit the data store and turn off Snapshots, at which point a Service Account will be required to authenticate the data store.
Using a Netskope DSPM Service Account
Begin by configuring a MySQL service account which will be dedicated to Netskope DSPM’s use. Authentication to RDS is supported using either IAM-based or password-based authentication.
Configure RDS
- As an administrator, log into your AWS RDS Console.
- Navigate to the database you wish to connect.
- Under the Configuration tab:
- Within the Summary section, make note of the Region value.
- Within the Instance section, ensure that the IAM Connectivity setting is enabled.
- Log into your MySQL database’s shell using these AWS instructions.
- Create the Netskope DSPM-specific MySQL user by executing the following commands in order:
| Command | Outcome | Notes |
|---|---|---|
CREATE USER '[USER]'@'%' IDENTIFIED WITH AWSAuthenticationPlugin AS 'RDS'; | Creates the Netskope DSPM-specific user for authentication using the AWS RDS plugin. | Substitute [USER] with your own preferred value.Note: @'%' creates a user which supports remote connection. As an alternative, substitute it with @'#.#.#.#' to limit to specific IP addresses. |
GRANT SELECT ON *.* TO '[USER]'; | Grants to the Netskope DSPM-specific user the required permissions which power capabilities within the Netskope DSPM platform. | Substitute [USER] with the value used above.Note: *.* means “on all schemas, in all tables in those schemas (current and future)”. |
Configure IAM
- As an administrator, log into your IAM Dashboard.
- In the left-hand menu, select Roles.
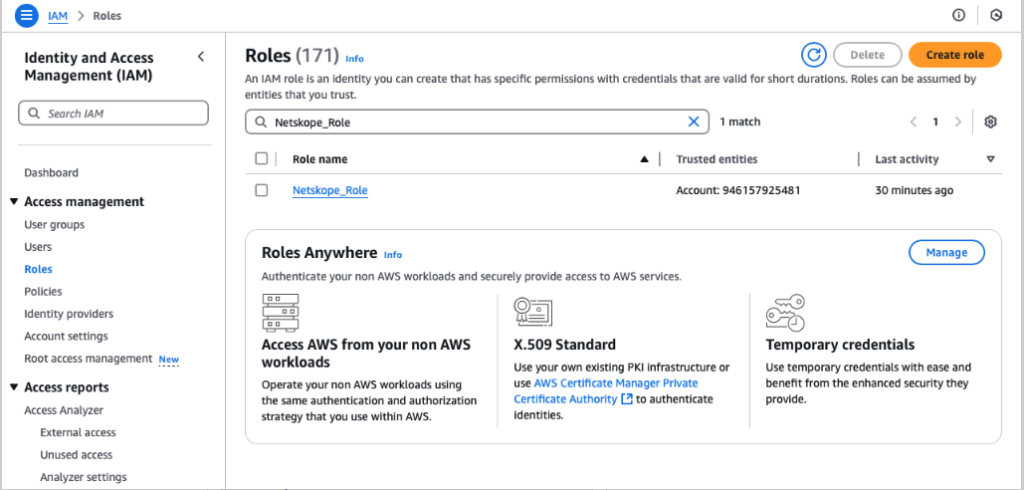
- Using the search box, find and open the Netskope-specific role. (Most likely named “Netskope_Role” if created using the Netskope CloudFormation or Terraform script. Otherwise, create a custom role with the same Trust Relationship) .
- Under the Permissions tab, click Add Permissions > Create inline policy.
- On the Specify Permissions screen, click the JSON button.
- In the Policy editor section, overwrite the default JSON with the following code. Replace
[REGION],[ACCOUNT], and[USER]with your specific values:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": [
        "rds-db:connect"
      ],
      "Resource": [
        "arn:aws:rds-db:[REGION]:[ACCOUNT]:dbuser:*/[USER]"
      ]
    }
  ]
}
- Click Next.
- On the Policy Details screen, enter a Policy Name (e.g.,
Netskope_Policy_RMSto clarify its purpose). - Click Create policy.
- As an administrator, log into your MySQL database’s shell using these AWS instructions.
- Create the Netskope DSPM-specific MySQL user by executing the following commands in order:
| Command | Outcome | Notes |
|---|---|---|
CREATE USER '[USER]'@'%' IDENTIFIED BY 'netskope_password'; | Creates the Netskope DSPM-specific user for authentication using a password. | Substitute [USER] and netskope_password with your own preferred values.Note: @'%' creates a user which supports remote connection. As an alternative, substitute it with @'#.#.#.#' to limit to specific IP addresses. |
GRANT SELECT ON *.* TO '[USER]'; | Grants to the Netskope DSPM-specific user the required permissions which power capabilities within the Netskope DSPM platform. | Substitute [USER] with the value used above.Note: *.* means “on all schemas, in all tables in those schemas (current and future)” |
Configure Query Logging (Optional)
Netskope DSPM’s Data-In-Use-Monitoring capability requires access to query logging. If you wish to leverage this capability, you must configure your MySQL instance to begin generating such logs.
– Users with the MySQL permission to set the
sql_log_off session variable can disable logging for their own session. For optimal security, restrict access to this setting.– These changes require a MySQL server restart. We recommend scheduling this reboot during a maintenance window.
- Log into your AWS RDS Console.
- Under Amazon RDS in the left-hand menu, navigate to Parameter groups.
- Select an existing parameter group for your MySQL database (or create a new one using these AWS instructions).
- Click Edit parameters.
- Using the search box, find the following parameter keys and set their corresponding values:
| Parameter Key | Value |
|---|---|
general_log | On |
log_output | TABLE |
- Click SAVE.
- Log into your MySQL database’s shell and execute the following command to manage log rotation:
| Command | Outcome |
|---|---|
CALL mysql.rds_rotate_general_log; | Deletes the mysql.general_log_backup table, renames mysql.general_log to general_log_backup, and creates a new mysql.general_log table.Note: To limit the size of logs, AWS RDS calls this function whenever logs exceed 10GB or 10% of database space. You can also configure your MySQL server to call this function on a regular cadence. |
- Restart your MySQL server at your earliest convenience.
Retrieve Connection Information
In addition to configuring a service account, Netskope DSPM will also require additional information in order to communicate with your MySQL instance.
- Log into your AWS RDS Console.
- Under Amazon RDS in the left-hand menu, navigate to Databases.
- For the database you wish Netskope DSPM to scan, click its link in the DB Identifier column. (For Aurora MySQL, be sure to choose a database with Role = “Writer Instance” instead of “Regional cluster”).
- In the Connectivity & security section, make note of the following values from your console:
| Corresponding Netskope DSPM Value | Where to find it in AWS Console |
|---|---|
| Data Store Endpoint | Endpoint |
| Data Store Endpoint (Port) | Port |
Connect Your Data Store
Follow these steps to configure the connection:
Step 1: Provide Credentials
- Go to Data Stores > Data Store Inventory.
- Click CONNECT A DATA STORE in the upper right.Tip: Alternatively, if the data store was already found by auto-discovery, go to the Discovered tab and click Connect in the Actions column.
- In the Connect a Data Store window, click the data store icon you wish to connect.
- In the Provide Credentials section, complete the following fields:
| Field | Value |
|---|---|
| Select AWS Account | Select one of the AWS Accounts defined within the Infrastructure Section screen. The field defaults if there is just one AWS Account configured. |
| Data Store Identifier | Provide a friendly name to describe this Data Store. |
| Data Store Endpoint | Enter the corresponding values from the Retrieve Connection Information step above, plus the port number. For example, for an address like example.rds.amazonaws.com, you would enter example.rds.amazonaws.com:3306. (Note: 3306 is the default MySQL port number. Substitute if you use a custom port) |
| Authentication Method | Select the desired authentication method. |
| Database Username | Enter the corresponding value from the Using a Netskope DSPM Service Account step above. |
| Password | When Authentication Method equals “Username / Password”, enter the corresponding value from the Password-based authentication step above. |
| Scan Frequency | Controls how often your Data Store is reviewed for changes. |
| Sidecar Pool | Select a sidecar pool with network visibility to said data store. |
- Click Next.
- When the Select Capabilities tab appears, complete the following fields:
- Assign a Data Owner (Optional): Select one or more users responsible for this data store.
- Which databases should Netskope DSPM scan?: Select the specific data stores and schemas to monitor, if applicable.
- Features: Select the features you want to enable.
| Capability | Supported for AWS Aurora MySQL via Service Account | Supported for AWS Aurora MySQL via Snapshots |
|---|---|---|
| Discovery | Yes (always-on) | Yes |
| Privilege Analysis | Yes Note: MySQL version 8.0 or higher is required. Disable for older versions | No |
| Shadow Data Analysis | Yes | No |
| Classification | Yes | Yes |
| Data In Use Monitoring | Yes Note: Query logging must be configured first | No |
| Automation | Yes (always-on) | Yes |
- Click Save. When the Review tab appears, the system validates your configuration. If there are any issues, follow the on-screen instructions to fix them .
- Click Save to finalize the connection.
Unable to access system logs for MySQL database, be sure to double-check your logging configurations in the Configure Query Logging section above.| Method | Benefits | Drawbacks & Limitations |
|---|---|---|
| Snapshots | A simple and quick setup. DSPM scans a secure, temporary, and encrypted copy of the data store without requiring database credentials. | Scan initiation can take several hours. This method does not support the following features: – Privilege Analysis. – Data-in-use monitoring. – Specific database selection. – Sample data collection. |
| Service Account (Recommended) | Enables all supported DSPM capabilities, including Privilege Analysis and Data-in-use Monitoring. | Requires additional configuration steps within your AWS database and may require administrator assistance. |
Step 2: Prepare Your AWS Aurora MySQL Database
Next, complete the necessary preparations in your AWS environment based on the authentication method and features you plan to use.
Create a Database User (If using a Service Account)
You only need to complete this section if you chose the Service Account authentication method in Step 1. You can authenticate the service account using IAM or a traditional password.
-
Enable IAM Database Authentication on your RDS instance:
-
Go to your AWS RDS Console > Databases.
-
Select the database you wish to connect.
-
Go to the Configuration tab > Summary section and save the Region value for later use.
-
In the Instance section, confirm that IAM Connectivity is enabled.

-
-
Create the MySQL user and grant permissions:
-
Log in to your MySQL database shell as an administrator using the AWS instructions.
-
Run the following commands:
Command Notes CREATE USER '[USER]'@'%' IDENTIFIED WITH AWSAuthenticationPlugin AS 'RDS';Outcome: Creates the user for IAM-based authentication.
– Substitute[USER]with your preferred username.GRANT SELECT ON *.* TO '[USER]';Outcome: Grants the user the required permissions to scan all current and future tables.
– Substitute[USER]with the username you created.
-
-
Configure the IAM Policy for the Netskope Role:
Follow these steps to create the specific IAM policy that allows DSPM to connect to the database user.
-
Go to the AWS IAM Console > Roles.
-
Find and open the role used for the Netskope integration.
– If you used Netskope’s CloudFormation or Terraform, the role is likely namedNetskope_Role.
– Alternatively, you can create a custom role, just make sure it uses the same Trust Relationship as the default Netskope role.Your should see something like to this:
-
Under the Permissions tab, select Add Permissions > Create inline policy.
-
When the Specify permissions page appears, select the JSON tab.
-
Overwrite any existing content by pasting the following JSON policy template into the editor.
{ "Version": "2012-10-17", "Statement": [ { "Effect": "Allow", "Action": [ "rds-db:connect" ], "Resource": [ "arn:aws:rds-db:[REGION]:[ACCOUNT]:dbuser:*/[USER]" ] } ] } -
In the policy editor, replace the following placeholder values with your specific AWS information:
Placeholder Value [REGION]The AWS region where your RDS database resides. [ACCOUNT]Your AWS account number. [USER]The DB username you defined in the MySQL shell. For Multi-Region Support: If you plan to connect with RDS databases in more than one AWS region, add an additional row to the `Resource` object for each region. For example:"Resource": ["arn:aws:rds-db:us-east-1:[ACCOUNT]:dbuser:*/[USER]","arn:aws:rds-db:us-west-2:[ACCOUNT]:dbuser:*/[USER]"] ```Your screen should now look similar to this:

-
Click Next.
-
On the Policy Details screen, for Policy Name, enter a descriptive name (e.g.,
Netskope_Policy_RMS). -
Click Create policy.
-

-
Log in to your MySQL database shell as an administrator using the AWS instructions..
-
Run the following commands:
Command Notes CREATE USER '[USER]'@'%' IDENTIFIED BY '[PASSWORD]';Outcome: Creates the user for Netskope DSPM.
– Substitute[USER]and[PASSWORD]with your own secure values.GRANT SELECT ON *.* TO '[USER]';Outcome: Grants the user the required permissions to scan all current and future tables.
– Substitute[USER]with the username you created.
Configure Query Logging (for Data-In-Use Monitoring)
Complete this section only if you plan to enable the Data-In-Use Monitoring feature, which is available when using the Service Account authentication method from Step 1.
If you meet these conditions, complete the following setup:
-
Set Query Logging Parameters:
-
Go to the AWS RDS Console > Parameter groups.
-
Select the parameter group for your MySQL database. If one does not exist, create one.
-
Click Edit parameters.
Flag Value general_log On log_output TABLE -
Click Save changes.
-
-
Rotate Logs:
-
Log in to your MySQL database shell as an administrator using the AWS instructions.
-
Run the command:
CALL mysql.rds_rotate_general_log;This AWS RDS function first deletes any existing backup log table (mysql.general_log_backup), then renames the current log table (mysql.general_log) to become the new backup, and finally creates a newemptymysql.general_logtableto receive new log entries.
-
-
Restart the MySQL Server:
-
Restart your MySQL server at your earliest convenience for the logging changes to take effect.
-
Step 3: Retrieve Connection Information
(This section is identical to the PostgreSQL article and is a candidate for an excerpt).
Next, gather the required connection details from AWS.
- Go to the AWS RDS Console > Databases.
- Click the link for your database in the DB Identifier column.
- Note: For Aurora MySQL, choose a database with Role = “Writer Instance”.
- In the Connectivity & Security section, copy the following values:
Step 4: Connect the Data Store
Finally, use the information you prepared to connect the data store in the Netskope One console.
- Go to Data Stores > Data Store Inventory.
- Click CONNECT A DATA STORE.
- On the Select Data Store tab, click the AWS Aurora MySQL icon.
- The Provide Credentials tab appears, complete the following fields:
| Field | Value |
|---|---|
| Select AWS Account | Select the AWS Account configured in Infrastructure Connections. |
| Data Store Identifier | Enter a friendly name for this data store. |
| Data Store Endpoint | Enter the Endpoint and Port from Step 3. For example, if your address is example-endpoint.us-west-2.rds.amazonaws.com, you would need to add :port at the end like example-endpoint.us-west-2.rds.amazonaws.com:3306Note: 3306 is the default MySQL port number. If you are using a custom port number, be sure to substitute it here. |
| Authentication Method | Select the method you configured: IAM or Username / Password. |
| Database Username | (If using Service Account) Enter the username you created in Step 2. |
| Password | (If using Password authentication) Enter the password for the service account user. |
| Scan Frequency | Select how often DSPM reviews the data store for changes. |
| Sidecar Pool | If you use sidecars to monitor this data store, select a sidecar pool with network visibility to it. To learn more, please visit our Sidecar Administration article. |
- Click Next.
- When the Select Capabilities tab appears, complete the following fields:
- Assign a Data Owner (Optional): Select one or more users responsible for this data store.
- Which databases should Netskope DSPM scan?: Select the specific databases and schemas to monitor.
- Features: Select the features you want to enable.
| Capability | Supported via Service Account | Supported via Snapshots |
|---|---|---|
| Discovery | Yes (always-on) | Yes |
| Privilege Analysis | Yes (Note: MySQL version 8.0 or higher is required) | No |
| Shadow Data Analysis | Yes | No |
| Classification | Yes | Yes |
| Data In-Use Monitoring | Yes (Note: Query logging must be configured) | No |
| Automation | Yes (always-on) | Yes |
- Click Save.
- When the Review tab appears, the system validates your configuration. If there are any issues, follow the on-screen instructions to fix them.
- Click Save to finalize the connection.