

Note
This feature is available with IPSec, GRE, Netskope Client, or DNSaaS access methods.
405: “method not allowed, please contact support to migrate v1 DNS Profiles”
If this error is seen, please reach out to the Netskope customer support team at support@netskope.com
DNS profiles allow you to control, inspect, and log all or blocked DNS traffic. When configuring a DNS profile, you can configure the actions taken for specific domain categories and choose to allow or block specific domains. Additionally, you can choose to block all DNS tunnels and select DNS tunnels to exempt.
To create a DNS profile:
-
Navigate to Policies > DNS.
-
Click New DNS Profile. The DNS Profile page appears.
-
Enter a name for the DNS profile.
-
Select your Inheritance Group. Click the field to search for it.
-
Select whether to generate events for Only blocked DNS traffic or All DNS traffic.
-
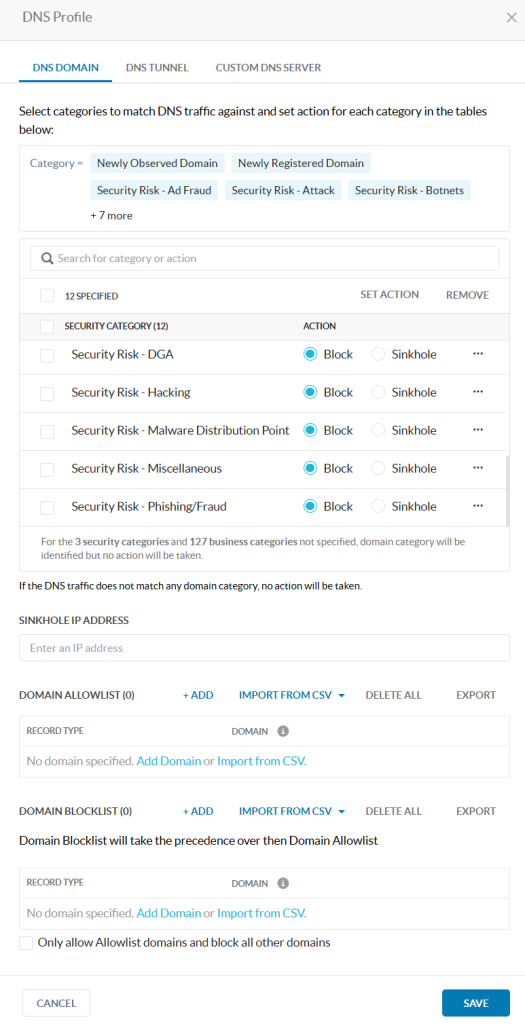
Under the DNS Domain tab, you can do the following:
-
Select Category. Instead of entering and blocking domains one by one, select a category and choose what Netskope should do with DNS queries for domains in that category.
Available Categories are:
-
Security Category: Domains that pose a security threat. For example, Phishing or Newly Registered Domains.
-
Business Category: Groups domains by their purpose or content, such as social networking or streaming.
-
-
Select Action to determine how Netskope handles DNS queries for domains in the selected categories. Select one of the following:
-
Block: Blocks DNS queries for domains in that category.
-
Sinkhole: Returns the configured Sinkhole IP Address instead of the domain’s actual IP address.
-
-
If you chose Sinkhole as the action for a domain category, enter a Sinkhole IP Address.
-
For the Domain Allowlist and Domain Blocklist fields, you can specify the domains you want to allow or block.
For each domain, you must specify a Record Type or select All Record Types.-
For the Domain Allowlist and Domain Blocklist fields, you can specify the domains you want to allow or block all DNS requests from.
For the domain, you must specify the Record Type or choose All Record Types. You can click + Add to add more domains or click Import From CSV to upload a CSV file (the maximum upload is 8 MB).
To learn more, see DNS Record Type.
The Domain Blocklist takes precedence over the Domain Allowlist.
-
-
Select Only allow Allowlist domains and block all other domains to restrict DNS queries to allowlisted domains.
This option uses the Domain Allowlist as the exception list. A query must match both the domain and the record type configured in an allowlist entry. Select All Record Types to match any record type for that domain.
-
-
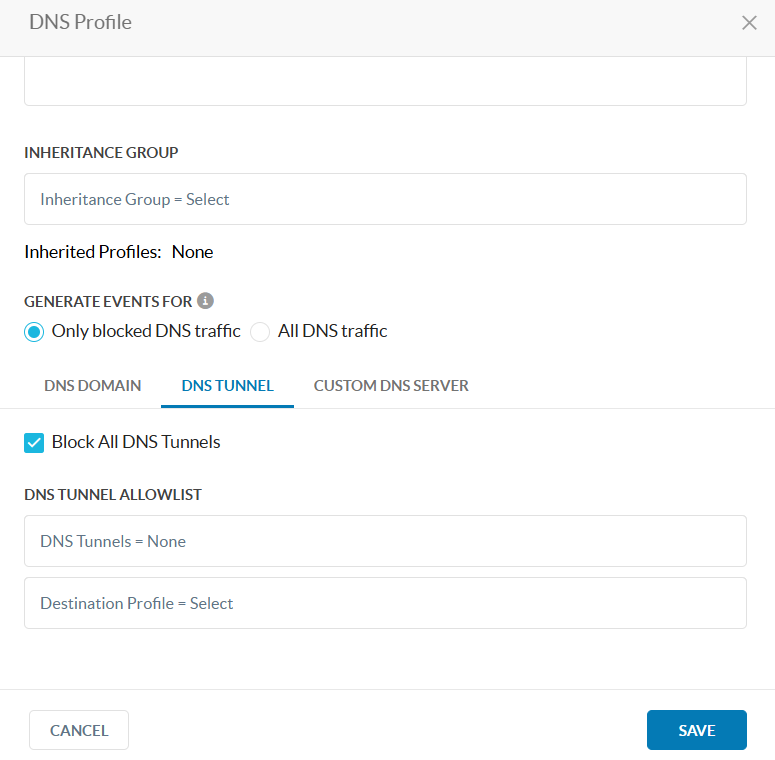
Under the DNS Tunnel tab, enable Block All DNS Tunnels.
-
Under DNS Tunnel Allowlist select DNS Tunnels that you want to allow.
-
Select Destination Profile that contains the domains you want to exempt from tunnel blocking.
- Contact Netskope Support to get the Destination Profile feature enabled.
- Domains added to the DNS tunnel allow list through Destination Profile are exempt from DNS tunnel blocking, even if DNS tunneling is detected on them. To learn more, see Destination Profile.
-
-
Under Custom DNS Server, you can enable the Custom DNS Server functionality and enter up to five public IPv4 addresses separated by commas or new lines for forwarding the DNS traffic. The DNS servers are evaluated in the order you enter them.
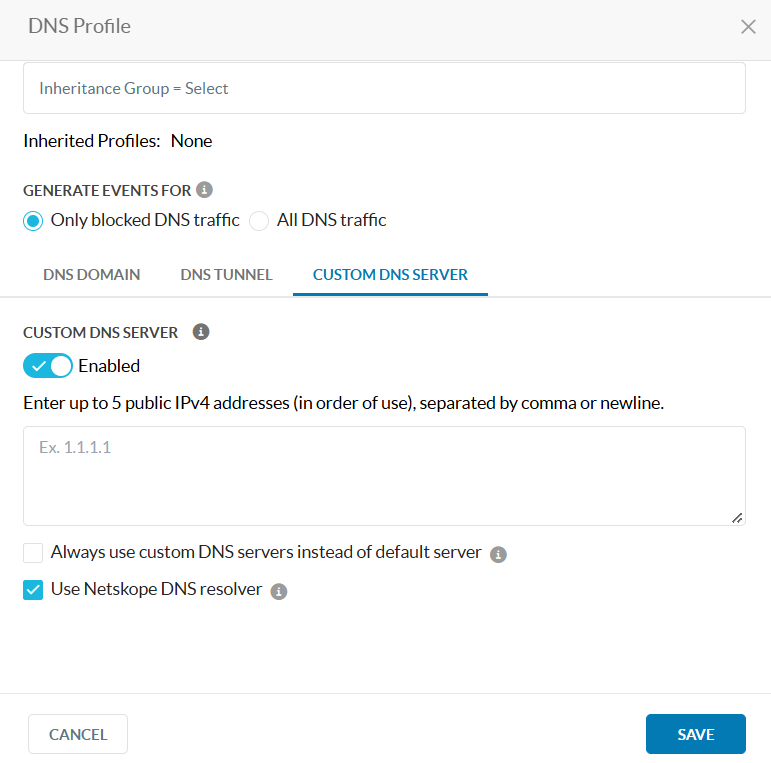
Netskope will forward the destination to these DNS servers for resolution when the default DNS servers are private, unreachable from Netskope cloud, or rejecting the requests.
The Always use custom DNS servers instead of default server option will replace the destination address with the custom DNS server’s IP address for all DNS traffic.
The Use Netskope DNS resolver option will use Netskope’s internal DNS resolver if the default and custom DNS servers fail. -
Click Save to save the DNS profile.
Non-DNS TCP application traffic sent over port 53 are assumed to be DNS traffic and treated accordingly.
Custom DNS server cannot be changed in the middle of TCP flow if server is marked as unreachable during flow’s lifetime as this requires a new connection sequence with the new server.
After you create a DNS profile, you must add it to a Real-time Protection policy. To learn more: Real-time Protection Policies.
Destination Profiles and Inheritance Groups

Destination Profiles replace the current domain lists used in Allowlist and Blocklist.
This feature also enables support for Inheritance Groups, using which you can add a number of DNS profiles as Parent profile – which can be Protected or Unprotected. The DNS profiles in the Inheritance Group are evaluated in addition to the Child DNS profile from the matched Real time policy rule.
Terminology:
- Child DNS Profile – DNS Profile used in the matched Real Time Policy rule
- Parent DNS Profiles – A group of DNS Profiles which are categorized as “Protected” or “Unprotected”
- Protected Parent DNS Profiles – The Parent DNS Profiles whose action can’t be overridden by the Child DNS Profile. Evaluated before Child DNS Profile is evaluated
- Unprotected Parent DNS Profiles – The Parent DNS Profiles whose action can be overridden by the Child DNS Profile. Evaluated after Child DNS Profile is evaluated
- Inheritance Group – As entity where Parent DNS Profiles can be added in “Protected” or “Unprotected” groups
To create an Inheritance Group:
-
Click Inheritance Groups > New Inheritance Group.

-
Fill in the Inheritance Group Name and select which Protected Parent DNS Profiles and Unprotected Parent DNS Profiles.
Child DNS Profiles override Unprotected Parent DNS Profiles but are overridden by Protected Parent DNS Profiles