

The File Type Detection capability allows admins to configure policies to allow or block files based on file name or extension, a specific category (e.g. binary or executable), file type (e.g. Android Package Kit), or file size. Optionally, admins can send files for deep analysis using DLP or Threat Protection Profiles or create Real-time Protection policies to ensure the content of files are checked to avoid data exfiltration or malicious files.
To analyze files exceeding the default size, you can enable Advanced File Scanning, also known as Large File Support (LFS). This feature allows you to modify file size limitations and timeout values. To learn more, see: Advanced Content Scanning.
Note
If LFS is enabled, Netskope performs data tricking during content inspection, sending small amounts of data to the client or server while processing the file. This prevents a connection reset due to a request timeout from the client or server during this process.
When Real-time Protection blocks a download of a large file, Netskope will terminate the connection. However, some clients might attempt to initiate a partial content request (i.e., retry to download the file’s remaining data.
The block partial content request feature blocks these partial requests.
Configuring File Constraints
To configure file constraints:
Note
The Real-time Protection policy supports up to 256 MB for restricting file types and file sizes by default. For extended file size support of up to 400 MB, reach out to your account team to enable this capability.
- Create a Real-time Protection policy or edit an existing policy. To learn more: Real-time Protection Policies.
- Click Add Criteria & Constraints and select File Constraints.

- Configure the following file constraints for the policy:
File Name or Extension
Use this option to restrict browsing, downloading, or uploading files based on file name or the file extension.
- Select whether the file should match or not match the conditions specified.
- Click Add File Name or Extension.

- In the Select File Name or Extension window, select if the matches are Case Sensitive. Then enter the file names with extensions, separated by commas (e.g., data.text,*.pdf). Alternatively, you can click Import from CSV to upload the file names and extensions.
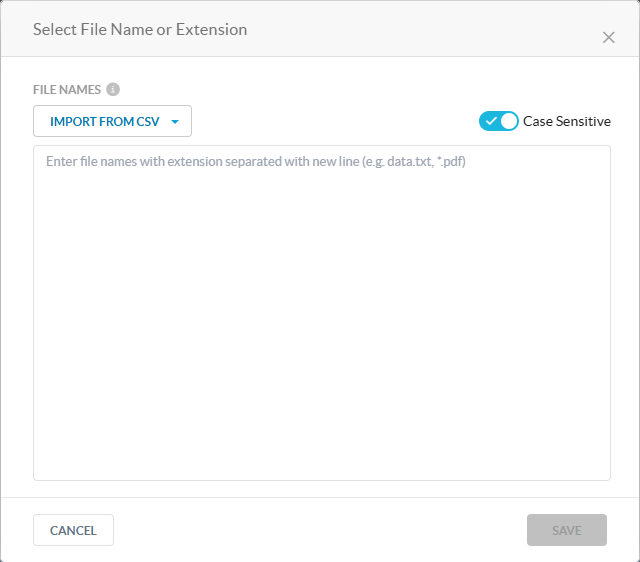
- Click Save.
File Type
Use this option to restrict browsing, downloading, or uploading files based on various types of files or categories of files.
- Select whether the file should match or not match the conditions specified.
- Click Select File Type.

- In the Select File Type window, select a category or click the magnifier to view and select the file types within the category.

- (Optional) Click Categories to return to the Category list without making any changes.

- (Optional) Select the File Type Not Detected category if your file category is an unknown file type or doesn’t fall into an existing categorization. Scroll to the bottom of the list to view this category.

- Click Save.
File Size
Use this option to restrict the size of various types of files or categories of files that users can browse, upload, or download.
- Select whether the file should match or not match the conditions specified.
- Select an operator for the File Size criteria.

- Enter a value and select the unit of measurement for the File Size criteria. You can enter up to 1024 GB for the file size.

- Configure the Profile & Action.
- Add a policy name.
- Click Save.


Tip
You can view generated alerts in the Skope IT Application Event Details panel. Navigate to Skope IT > Application Events to view alert details. To learn more, see Application Events.