

Issue
Microsoft has established cloud.microsoft as a unified, purpose-managed domain for Microsoft SaaS applications, services, and APIs. Many Microsoft 365 and Microsoft Copilot experiences use cloud.microsoft, with more experiences transitioning to this domain over time.
Microsoft recommends bypassing SSL decryption and inspection for Microsoft 365 traffic.
Netskope’s existing policy, Default Microsoft App Suite SSL Do Not Decrypt Rule, already includes the wildcard *.cloud.microsoft. However, this policy combines *.cloud.microsoft with more than 200 individually maintained domains, which makes it difficult to apply a targeted bypass specific to Microsoft 365 and Copilot traffic.
Solution
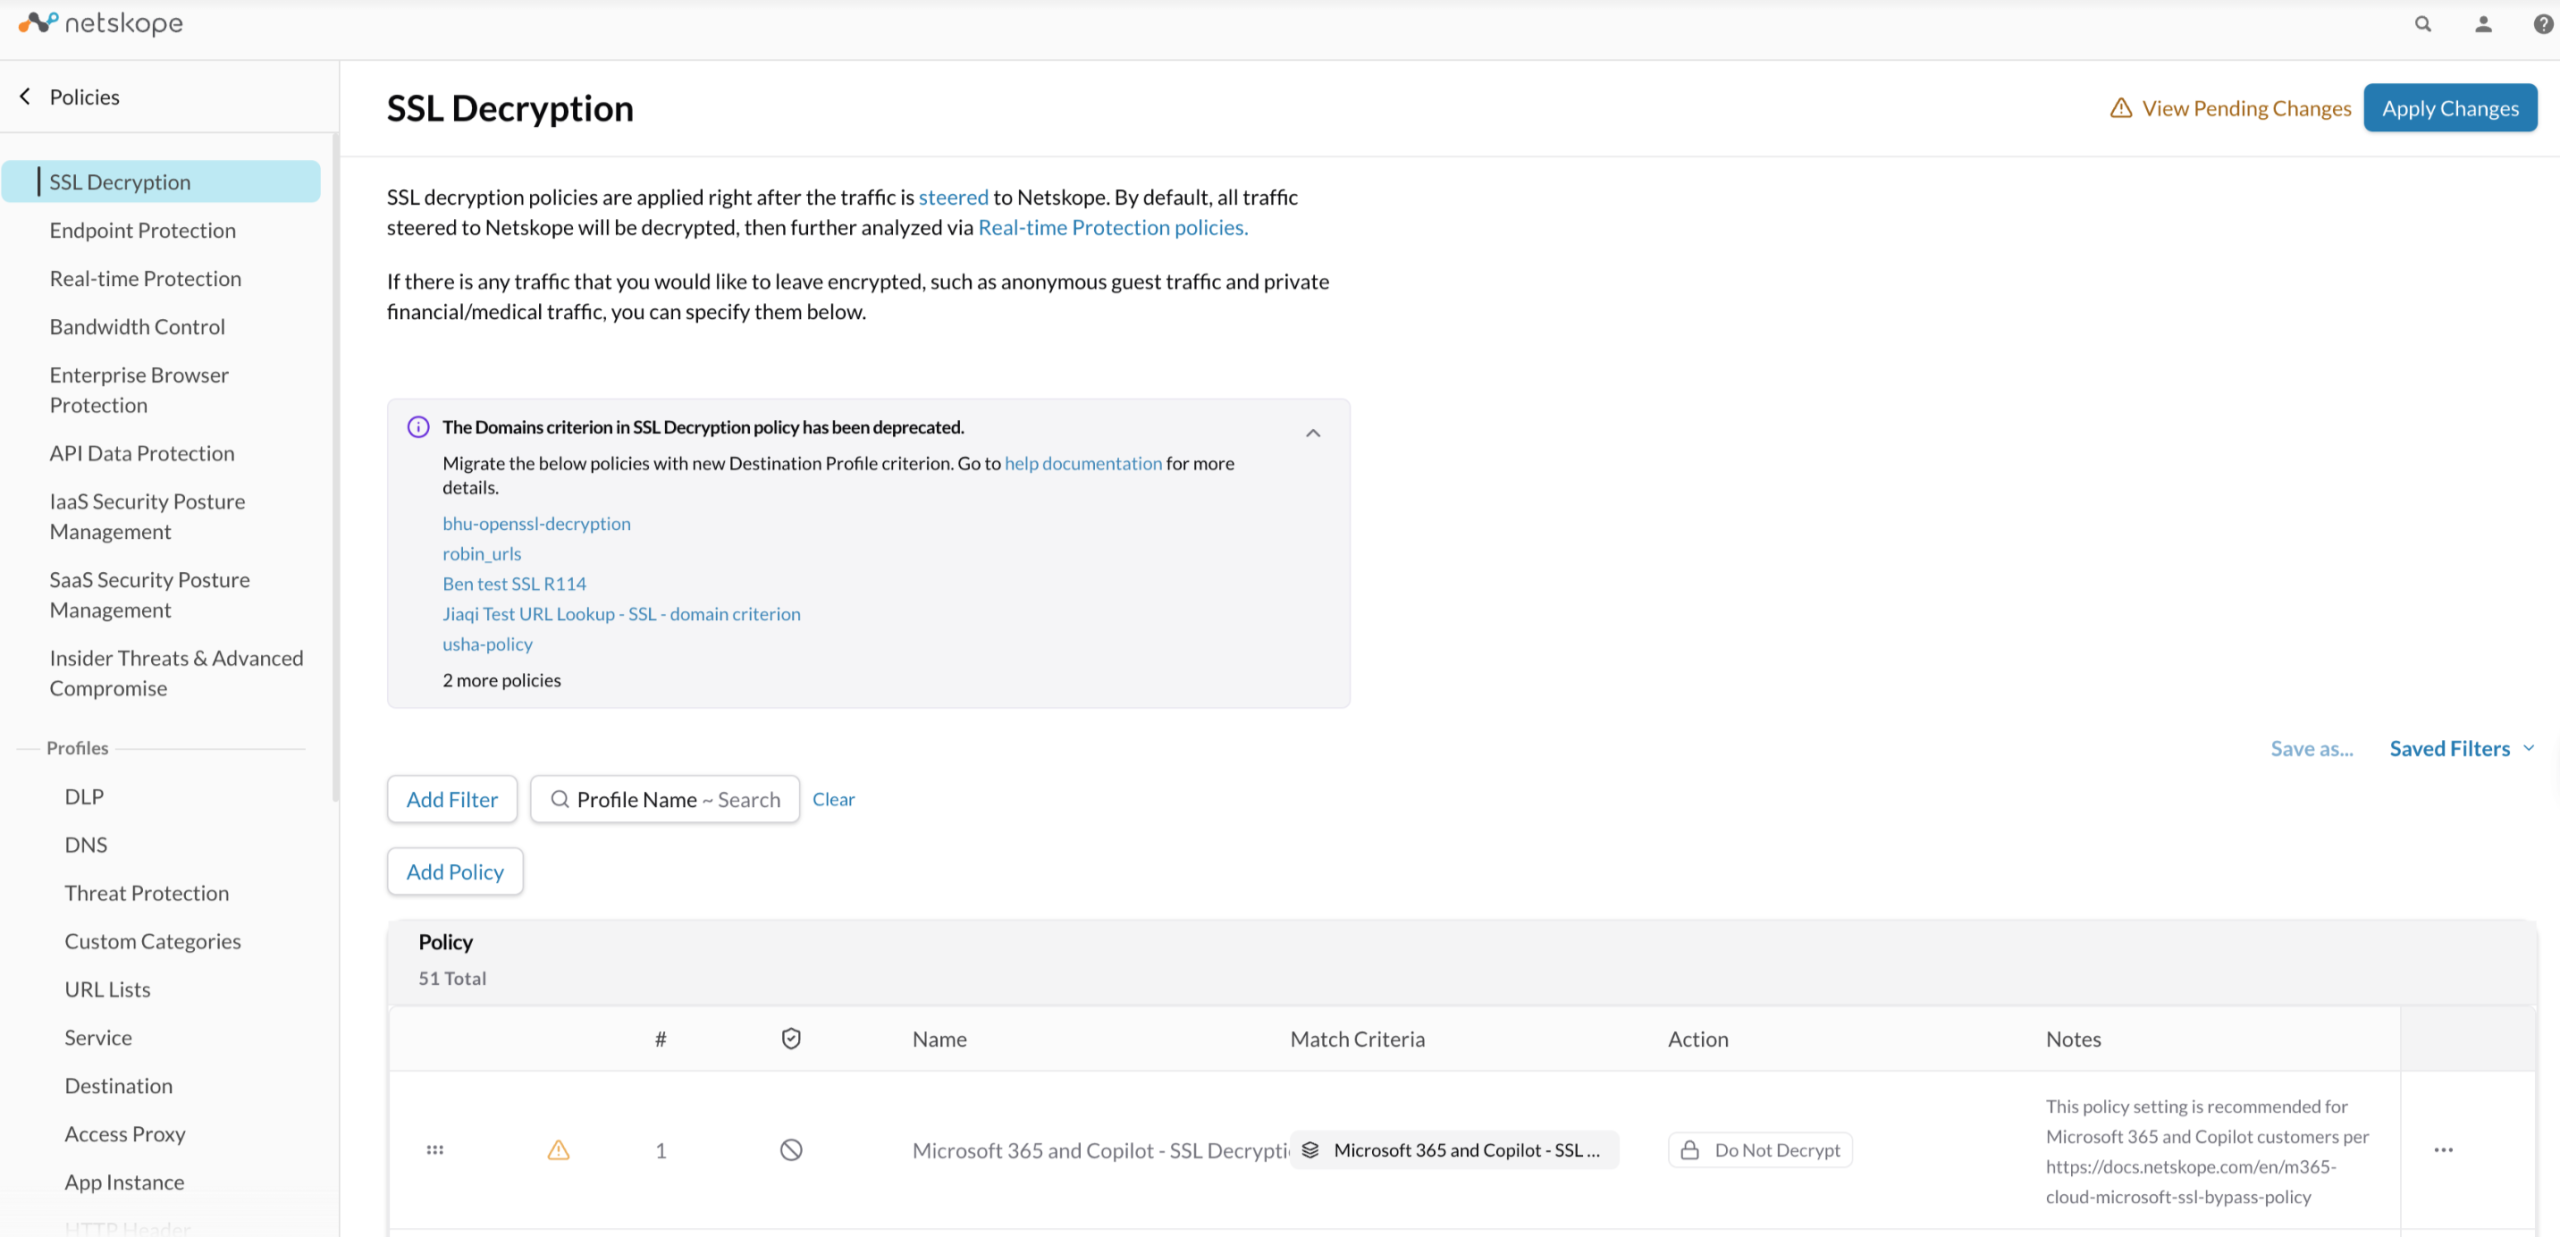
To provide a more targeted and easier-to-manage option, Netskope has introduced a new SSL bypass policy, Microsoft 365 and Copilot – SSL Decryption Bypass, preconfigured with a narrowly scoped domain set that currently includes only *.cloud.microsoft. Customers can simply enable this policy without manually adding the domains and can optionally add additional domains as needed.
The domains Microsoft recommends bypassing may be updated over time; Netskope will revise the preconfigured list to reflect that guidance.
If more than one bypass policy applies to *.cloud.microsoft, policy order determines the outcome. When enabling this policy, confirm it is placed at the appropriate priority so it takes effect as intended.
Microsoft Reference
- Information about cloud.microsoft domain. https://aka.ms/cloud.microsoft
- Microsoft recommendation to exempt Microsoft 365 traffic from TLS decryption: https://aka.ms/m365_tls_decryption_guidance
Policy Impact
-
If the policy is enabled, connections to *.cloud.microsoft bypass SSL decryption.
-
If the policy is disabled, connections to *.cloud.microsoft continues to be inspected. Traffic remains subject to other applicable Netskope security policies regardless of this setting.
Why This Setting is Provided
This setting lets customers align with Microsoft’s recommendation to bypass SSL decryption and inspection for Microsoft 365 and Copilot traffic served under cloud.microsoft, without changing the broader, pre-existing Default Microsoft App Suite SSL Do Not Decrypt Rule. Enabling the policy exempts *.cloud.microsoft traffic from SSL decryption; leaving it disabled keeps that traffic subject to existing inspection. Microsoft’s guidance on this recommendation is available in the Microsoft Reference section above.
Where to Find This Setting
The Microsoft 365 and Copilot – SSL Decryption Bypass setting is available under Policies > SSL Decryption, as shown in the screenshot below.
If you have any questions regarding this setting, please contact your Netskope account team or open a support case for assistance.