
Server-side certificates are required to enable SSL inspection on the VPE forward proxy. VPE supports three categories of certificate configuration:
-
Bring Your Own Key (BYOK)
-
Self-signed certificates
-
Default tenant certificate (requires no configuration)
With connectivity now configured, set up server side certificates to enable SSL inspection. You can use either a self-signed CA certificate or a CA certificate preferably signed by the enterprise’s Root or intermediate CA. See Use your own CA Certificates.
Alternatively, VPE can generate a self-signed certificate without CA. See Generate a Self-signed Certificate without CA.
Prerequisites
-
Administrative access to the VPE CLI over SSH (nsshell, then configuration mode)
-
For BYOK: your own server certificate, private key, and (if applicable) an intermediate CA chain
Option 1: Bring Your Own Key (BYOK)
Use this option to configure your own server certificate and private key, signed by your enterprise’s CA.
To configure your own key:
-
Enter the command:
set dataplane forward-proxy server-cert
-
Copy and paste your CA certificate in the buffer, press Enter, then type
Ctrl-Dto exit. -
Enter the command:
set dataplane forward-proxy server-key
-
Copy and paste your private key in the buffer, press Enter, then type
Ctrl-Dto exit. -
Enter the command:
set dataplane forward-proxy server-intermediate-ca-chain
-
Copy and paste any additional certificates in the following order:
-
Server certificate (as provided in step 1)
-
Intermediate CA certificate
-
Root CA certificate
-
-
Press Enter, then type
Ctrl-Dto exit. -
Enter
saveand press Enter to save the configuration.
Option 2: Generate a Self-Signed Certificate
-
If you don’t have your own certificate, generate a self-signed certificate directly on the VPE node:
run request certificate generate forward-proxy self-signed city <city> common-name <common-name> country <country> days <days> email-address <email-address> organization <organization> organization-unit <organization-unit> state <state>
-
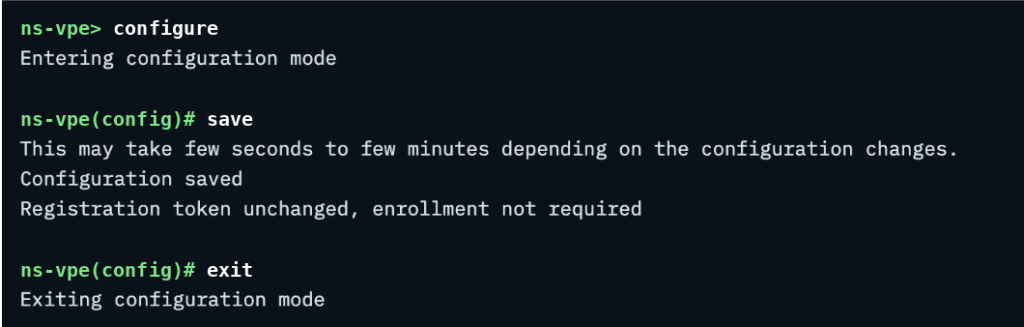
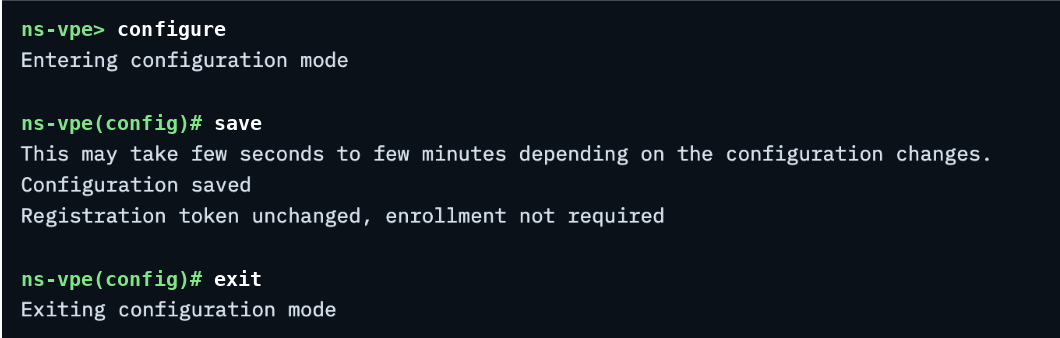
Enter save and press Enter to save the configuration.
After generating the certificate, enter configuration mode and save it.
Option 3: Default Tenant Certificate
If you do not configure a BYOK certificate or a self-signed certificate, VPE automatically uses the tenant’s default certificate, synced from the cloud. No configuration is required for this option.
Verify the Certificates
To verify that traffic routed through VPE is inspected with the certificate you configured, browse to any website and confirm that the SSL certificate presented is the certificate installed on the VPE node.