
After you deploying and registering the Virtual Private Edge (VPE) Node, you can now configure VPE and apply the Netskope service to your environment using templates. Templates in VPE let you define configuration once and apply it to many nodes, instead of configuring each node by hand.
Benefits of adding templates:
-
Configure once, apply to many: Especially at the group level, this is the main point of the whole system.
-
Separates infrastructure from security service config: Platform (NTP, OS upgrades) is independent of service (proxy rules, upgrade schedule for the SWG package itself), so one team can touch one without disturbing the other.
-
Two independent upgrade schedules: The node’s software and the service’s package version upgrade on separate clocks, each defined in its own template.
-
Consistent baseline across a fleet: Every node using the same template behaves identically, which is the point of standing up VPE at scale rather than one appliance at a time.
Configure a Platform Template
A platform template holds node-level settings that are the same for every node it is attached to: NTP servers and the software upgrade window.
To configure a platform template:
-
In the Netskope UI, go to Settings > Security Cloud Platform > On-Premises Infrastructure.
-
Click the Next-Gen tab.
-
On the Next-Gen page, click Manage Template > Platform Template.
-
In the Manage Template window, click New Template.
-
In the New Platform Template window, enter the required information such as the template name or NTP servers, enter the following details:
-
Enter the VPE Platform Template Name.
-
Enter one or more NTP servers, comma separated. For example, time.google.com.
-
Click the General Tab.
-
Under Upgrade timing, pick a frequency to schedule for upgrades. You can select one of the following: Daily, Weekly, or Monthly. Configure other values depending on the chosen frequency.
-
Select the Auto upgrade checkbox only to allow emergency upgrades outside the scheduled frequency.
-
Click the Advanced tab.
-
Toggle to select SNMP Agent.
Enable SNMP Agent if you want to monitor rest of the on-prem infrastructure, and wants VPE nodes to show up in that same single pane of glass.
-
Enter the following details:
-
System Contact (Email): Provide the system contact information (admin email etc). For example, admin@localskope.local.
-
System Location: Provide the system location. For example, “Los Altos HQ”.
-
SNMP Versions: Select either SNMP v2 or SNMP v3. The options under SNMP versions depend on the version that you choose.
-
If you choose SNMP v2
-
Community String: Provide a string value. The string configured here will be used in snmpwalk/snmpget commands from the SNMP manager to access the information exposed. If the value does not match the one configured, the relevant information will not be returned. It is used as access control in SNMPv2.
-
Allowed Network: (Optional) Provide the list of allowed hosts/subnets from where the SNMP status can be gathered.
-
-
If you choose SNMP v3
-
Engine ID: (Optional) Provide the engine identifier of the SNMP agent in hex format. For example, 0x0102030405.
-
Username: Provide the username to authenticate a user with the SNMP agent.
-
Authentication Protocol: Choose a hash function, “MD5” or “SHA” to store the data exchanged between the SNMP agent on the VPE and the SNMP manager.
-
Authentication Key: Enter the password required to connect with the SNMP agent.
-
Privacy protocol: (Optional) Choose an encryption type, “AES” or “DES” to encrypt the traffic between the SNMP agent on the VPE and the SNMP manager.
-
Privacy Key: (Optional) Set the password required to access the encrypted data on the SNMP agent.
-
-
-
Under SNMP Traps, configure SNMP traps on the VPE to send trap notifications to the SNMP trap receiver. Enter the following details:
-
Trap server: Provide the hostname or IP address of the SNMP trap receiver so that the VPE can send v2c or v3 traps.
-
Enable v2c Traps: Toggle to enable the VPE to send v2c trap notifications to the trap receiver.
-
Enable v3 Traps: Toggle to enable the VPE sends v3 trap notifications to the trap receiver.
-
Use Agent Settings: Toggle to enable this option if you want to use the same v3 usm authentication and privacy configurations as the SNMP agent. Else, configure v3 usm authentication and privacy for the trap client on VPE.
-
-
-
Click Save.
The VPE Platform Template column in Manage Template displays the template name for that node.
Attach Platform Template to a Node
To attach the created platform template to the VPE Node, on the Next-Gen page:
-
Click VPE Setup in the Services column for the VPE Node.
-
Click the VPE SetUp tab.
-
From the VPE Platform Template dropdown list, select the required platform template.
-
Click Save.
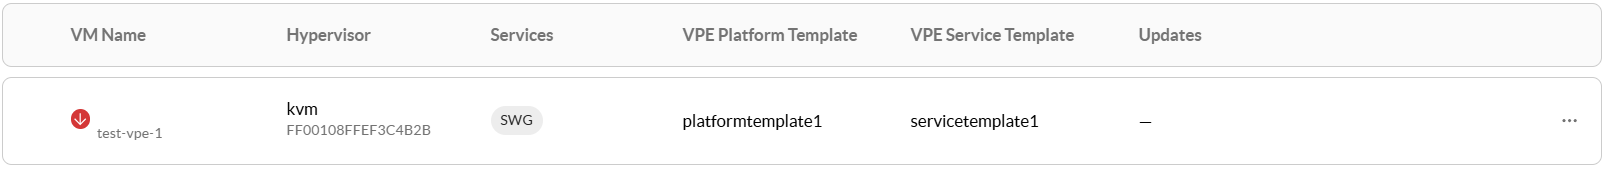
The name of the platform template appears in the VPE Platform Template column for the selected VPE Node.
Configure a Service Template
To create a service template:
-
In the Netskope UI, go to Settings > Security Cloud Platform > On-Premises Infrastructure.
-
Click the Next-Gen tab.
-
On the Next-Gen page, click Manage Template and then click Service Template.

-
In the Manage Template window, click New Template.

-
In the New Service Template window, enter the following information:
-
Enter the Service template name.
-
Under Upgrade timing, pick a frequency to schedule for upgrades. You can select one of the following: Daily, Weekly, or Monthly. Configure other values depending on the chosen frequency.
-
Select the Auto upgrade checkbox only to allow emergency upgrades outside the scheduled frequency.
-
Only Secure Web Gateway (SWG) and AI Guardrails are available as a supported service templates for VPE.
-
-
Under Services, select one of the following:
 SWGAI Guardrails
In the General tab and under Proxy Mode – Explicit, enter the Listener Ports. The default port is 8080.
-
Click the General tab.
-
Enter the following:
-
Under Proxy Mode – Explicit, set the Listener Ports. The default is 8080. You can also add multiple ports, for example, 8080, 8081, and so on.
-
Click to select the Enforce SAML Auth checkbox only if users must authenticate to the proxy.
-
-
Click the Advanced tab.
-
Toggle the following options to enable:
-
Under Advanced Forward Proxy: The following settings control two HTTP headers that get added to customer traffic when configured.
-
Use Client IP: Enable this option to use the header name X-Forwarded-For.
-
Client Identity: Enable this option to use the header name X-Authenticated-User.
-
-
Explicit Proxy Chaining:Forwards traffic from the VPE proxy to another proxy in your environment. Enable this option and provide the hostname and port of the upstream proxy. Once enabled, traffic reaches the VPE proxy first, then gets forwarded to the proxy you specified.
-
PAC Server: enable this option to direct cloud app traffic to the VPE node while other traffic continues through your existing proxy server. Enter the following:
-
Listener Port: Enter the TCP port to host the merged PAC file server.
-
Proxy Hostname (FQDN): Optionally, specify the fully-qualified domain name that resolves to the IP configured for the appliance. This host name will be used in the merged PAC file. If this setting is not provided, the appliance IP will be present in the merged PAC file.
-
Custom PAC Script: Enter the PAC script.
-
Custom PAC URL: Enter the URL of the existing PAC file server.
-
-
-
Click to select the System Features options:
-
Large File Support: Without this enabled, threat detection and file profiling applies only to files up to 16 MB, even though the proxy itself allows files up to 400 MB. Enable this option to extend threat detection up to the full 400 MB.
-
TSS Fast Scan: Enable this option to run threat detection on traffic passing through the proxy.
-
Health Check: Applies only when VPE nodes are deployed in a cluster of two or more nodes. It has no effect on a single, standalone VPE node.
-
-
TCP Optimization: Configure buffer size and throttle settings for TCP connections, as a Client and as a server:
-
Receive buffer size (Client only): default 1024 KB
-
Send buffer size (Client only): default 1024 KB
-
Throttle max threshold: default 1024 KB
-
Throttle min threshold: default 192 KB
-
-
Click Save.
For the AI Guardrails service, enter the following information:
-
HTTP (Port 8080): The port that the AI Guardrails On Demand API is available on.
-
GPU based AI Guardrails VM: Enable and connect to a GPU-based VM to leverage LLM based detection in AI Guardrails.
-
Association of the GPU based Container: Enter the container URL or IP address. Click GPU based AI Guardrails Image to download the GPU image.
-
JWT URL: (Optional) Enter the OAuth2 token endpoint, such as
https://<auth-provider>/oauth2/token. -
Client ID: (Optional) Enter the OAuth2 client ID issued by your identity provider (IdP).
-
Client Secret: (Optional) Enter the OAuth2 client secret issued by your identity provider (IdP). This field is obfuscated.
-
Scope: (Optional) Enter the OAuth2 scope.
-
AI Guardrails Certificate: Upload the certificate you want to use to securely connect to the AI Guardrails GPU-based VM.
-
-
Store Matched Content in Netskope: Enable to store the matched prompt/response content in Netskope to show in Skope IT Alerts and Incidents.

Field Remote Mode (OAuth 2.0) No-Token Mode jwt_url OAuth token endpoint URL Not present client_id OAuth client ID Not present client_secret OAuth client secret Not present scope OAuth scopes (optional) Not present
-
-
Click Save.
Attach Service Template to a Node
To attach the created service template to the VPE Node, on the Next-Gen page:
-
Click VPE Setup in the Services column for the VPE Node.
-
Click the VPE SetUp tab.
For SWG, this process can take up to 30 minutes to complete. As part of this process, the service image and its dependent images are automatically downloaded and deployed.
-
From the VPE Service Template dropdown list, select the required service template.

-
Click Save.
The name of the service template appears in the VPE Service Template column for the selected VPE-Node.
VPE Nodes Post Configuration
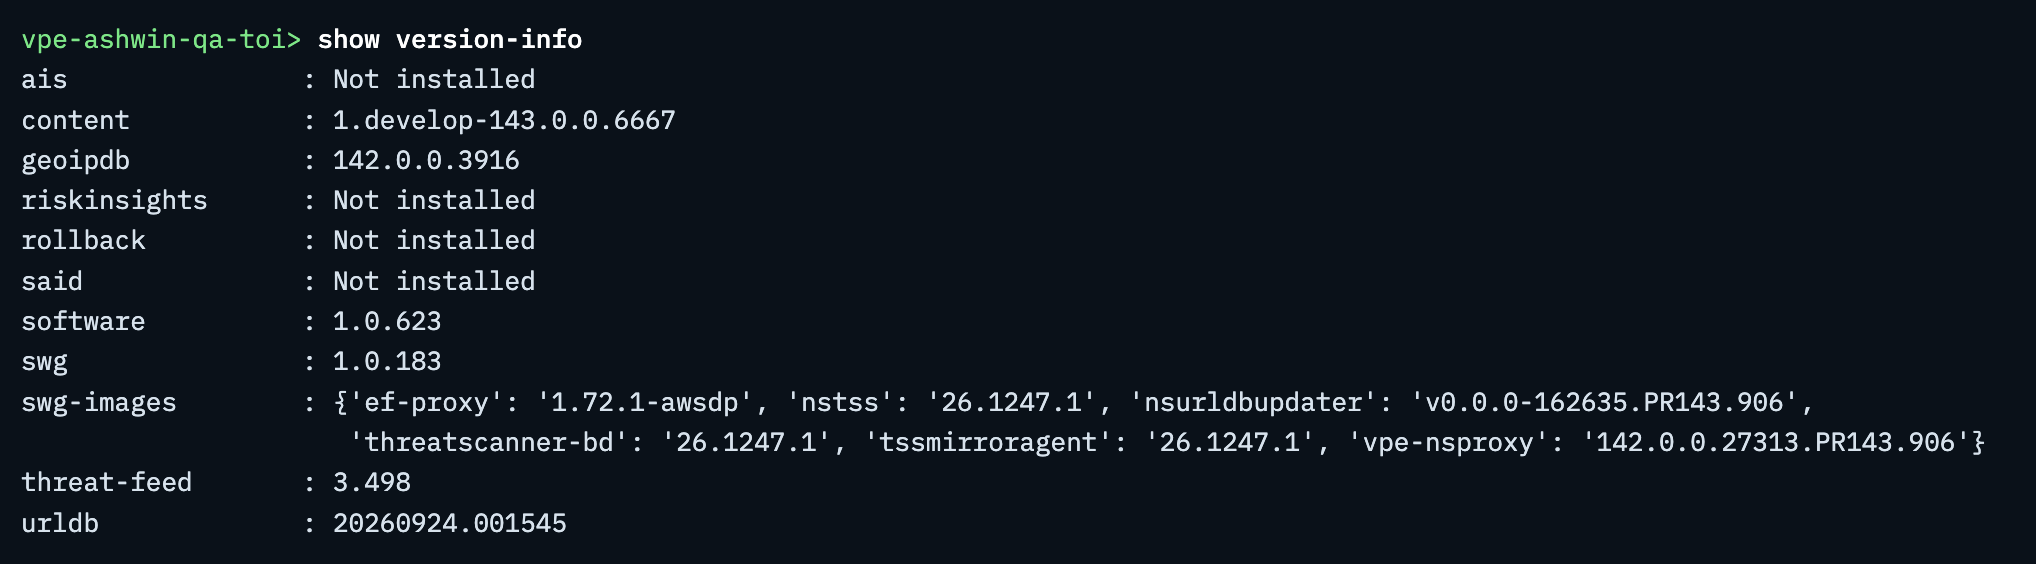
You can run show version-info to get the values for all attributes populated in the CLI.