

Threat Exchange is a rules-based engine for collecting and sharing indicators related to file hashes of malicious software (malware), file hashes of files used in Netskope DLP policy for absolute matching, or URLs used by plugged in systems for policy enforcement of restricted or allowed access. Indicators can be collected by a source plugin, or generated from Risk Exchange entity records and from unified mappings created in the Universal Schema Builder.
Click play to learn how to set up Threat Exchange.
Threat Exchange Global Settings
Only write-access users can change Threat Exchange Global Settings. Go to Settings > Threat Exchange. If the same IoC value is reported from different sources, then based on the reconciliation criteria, Threat Exchange will decide which IoC metadata should be kept and which will be ignored.
Reconciliation Criterias
Possible Reconciliation Criterias include:
- Always Overrides: If this criteria is selected, the latest IoC metadata will be kept in case of IoC Duplication.
- Never Overrides: If this criteria is selected, the oldest IoC metadata will be kept in case of IoC Duplication.
- Highest Severity Source Override: If this criteria is selected, the highest severity source’s IoC metadata will be kept in case of IoC Duplication.
Click play to watch a video.
IoC(s) Retraction
To enable IoC retraction from Cloud Exchange:
- Go to Setting > Threat Exchange.
- Enable the IoC(s) Retraction toggle and enter the Retraction Interval.
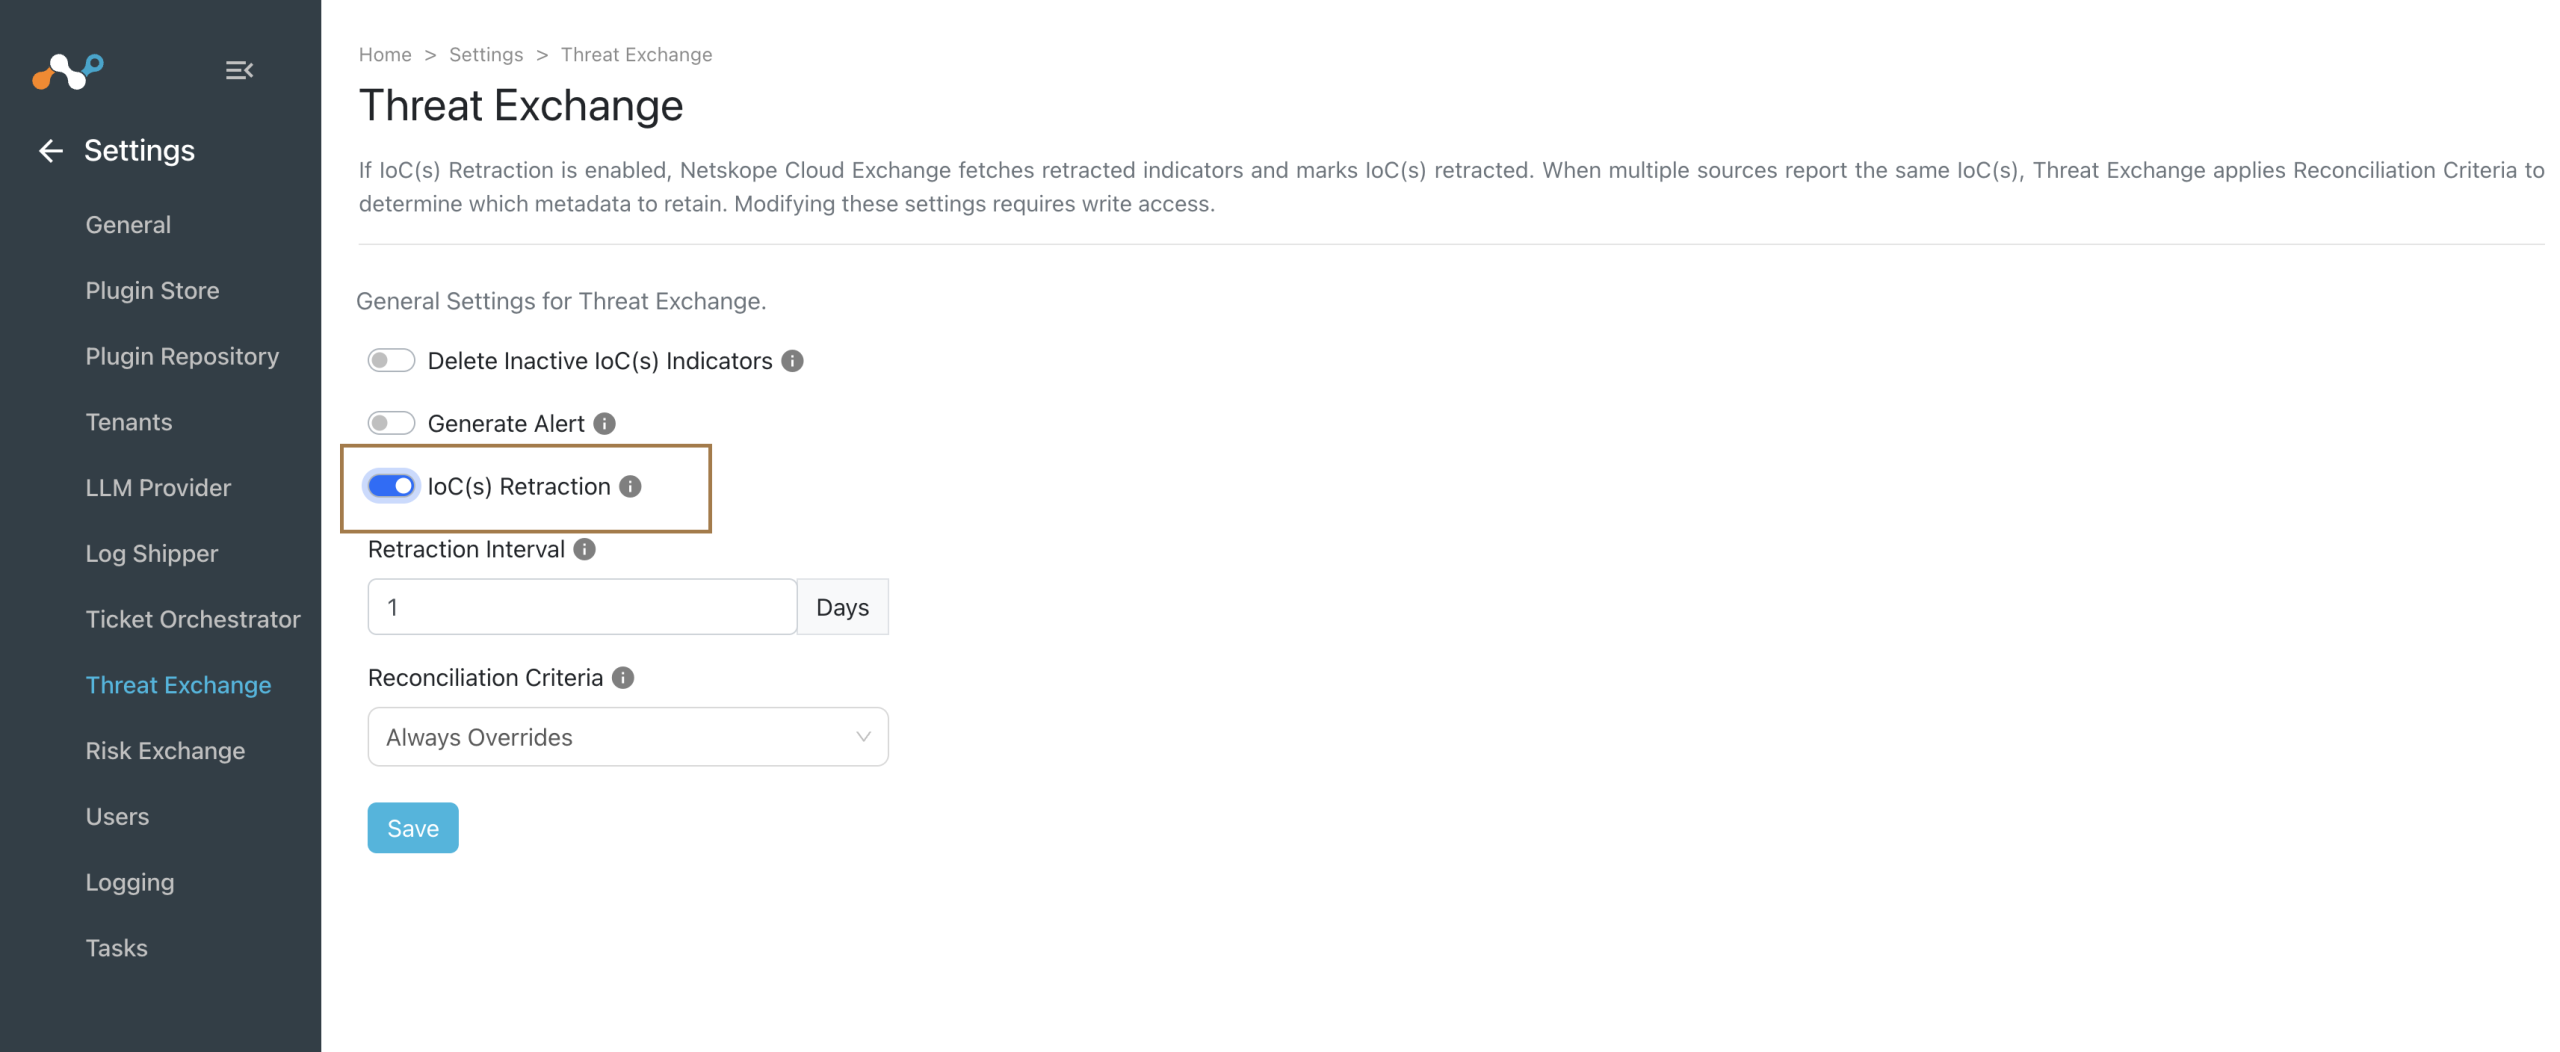
- Click Save.
Generate Alert
Go to Settings > Threat Exchange and enable Generate Alert to send alerts to the Ticket Orchestrator module when IoCs are shared. This setting applies to all sharing configurations:
- Enabled: Each sharing configuration generates alerts based on its own Generate Alert toggle. New sharing configurations have the toggle enabled by default.
- Disabled: No sharing configuration generates alerts, even if its own Generate Alert toggle is enabled. You cannot change the toggle on a sharing configuration until you enable this setting again.
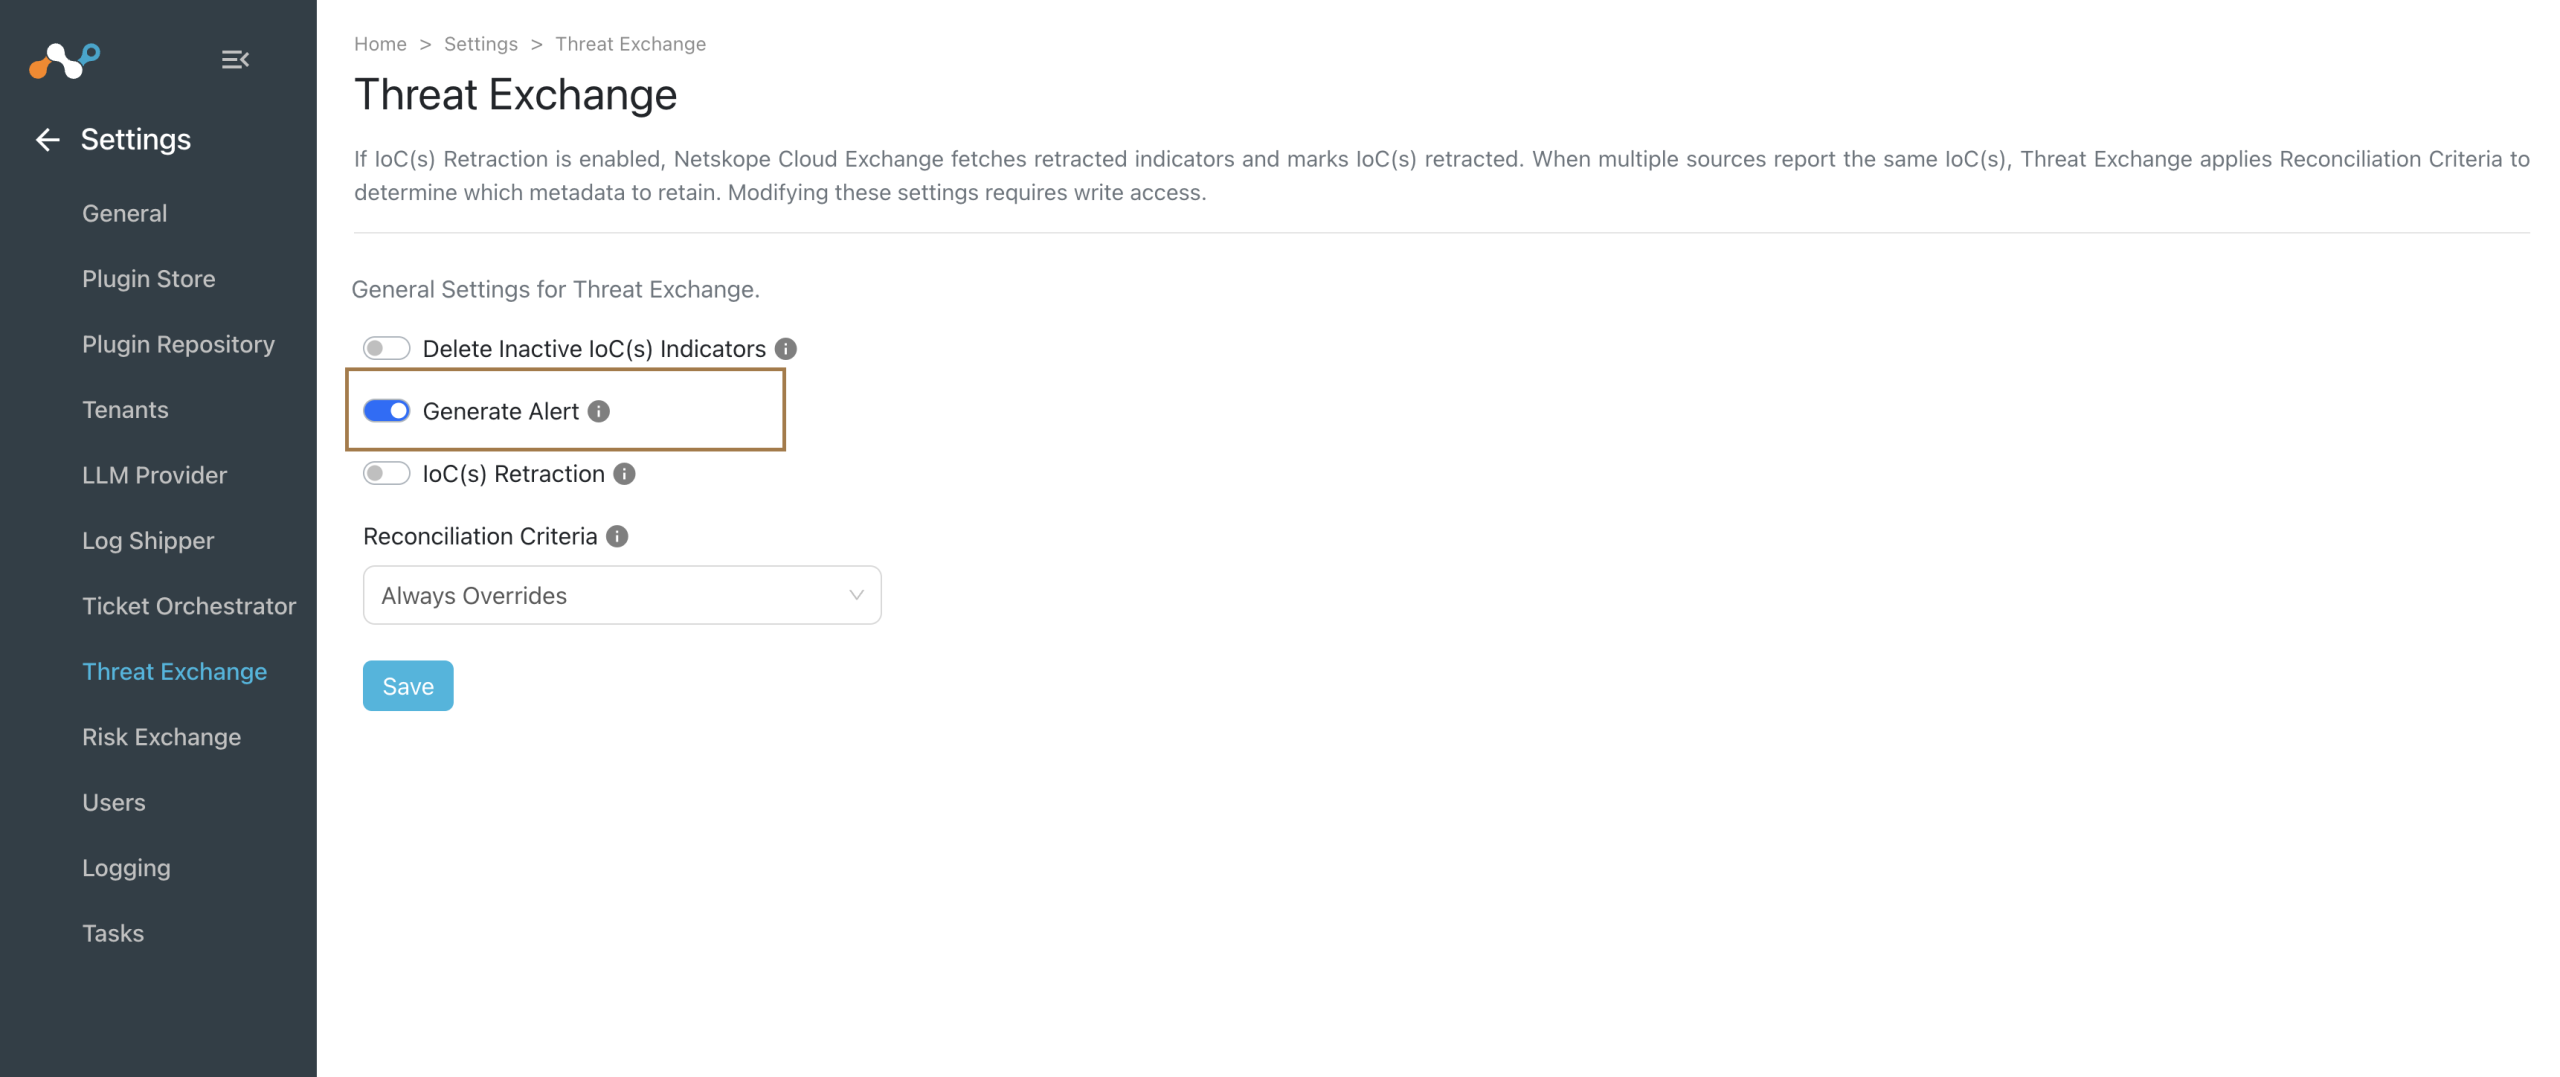
Alerts are generated only when the Ticket Orchestrator module is enabled in Settings > General. For details about the sharing configuration toggle, refer to Configure Threat Exchange IoC Sharing.
- Configure 3rd-party Threat Exchange Plugins
- Thales Plugin for Threat Exchange
- View Configured Threat Exchange Plugins
- Update Configured Threat Exchange Plugins
- Manage Threat Exchange Business Rules and IoC Sharing
- Configure your Netskope Tenant for Threat Exchange File Hash Sharing
- Manage Tags
- Threat Exchange Custom Plugin Developers Guide