

The Enhanced SAML Authentication feature introduces granular, service-specific control over authentication policies across different Netskope services. This replaces the legacy global SAML configuration model with a flexible, standards-compliant architecture tailored to enterprise security requirements.
Beginning with Netskope Client R134 and the Next Generation (NG) WebUI, administrators can configure Usage Profiles and Force Authentication to establish granular, service-specific authentication policies across services—such as enforcing mandatory step-up re-authentication for Private Access while preserving seamless Single Sign-On (SSO) for general web browsing. This capability provides:
-
Service-Specific Usage Profiles: Dedicated profiles for Internet Security, Cloud Firewall, Private Access (NPA), Borderless WAN (BWAN), and their respective re-authentication scenarios.
-
SAML 2.0 ForceAuthn Standard: Modern, standards-compliant re-authentication that instructs Identity Providers (IdPs) to enforce fresh verification regardless of active SSO sessions.
-
Automated Identity Hints: Streamlined login pre-population using login_hint and domain_hint parameters extracted from enrolled client certificates.
認証のためのSAML設定を構成する前に
Review the system requirements and operational guidelines before configuring SAML settings for forward proxy authentication.
Requirements and Prerequisites
| 成分 | Requirement Specification |
|---|---|
| Netskope Tenant | Release R134 or later; Next Generation (NG) WebUI enabled. |
| Netskopeクライアント | Version R134 or later installed on endpoints (Windows and macOS). Compatible client required for Borderless WAN. |
| Identity Provider (IdP) | Must support SAML 2.0 ForceAuthn specification and recognize login_hint / domain_hint query parameters. |
| Client Certificates | Enrolled client certificates must contain the user's email address or UPN within the Subject field to enable identity pre-population. |
重要な注意事項
-
Admin vs. Non-Admin Scope: Instructions in this section apply only to non-admin end users. To configure SSO for administrator access, refer to the Single Sign On for Administrators guide.
-
Partial Configuration (R121+): As of R121, IdP accounts can be partially configured and saved to retrieve the ACS URL and Netskope metadata, allowing easier setup in your third-party IdP.
-
REST API Provisioning: Creating and managing IdP accounts programmatically is supported via REST API v2. For endpoint and payload details, refer to the REST API v2 Configuration Reference section below.
Key Features and Capabilities
These enhancements are supported on tenants running Netskope Release R134 or later with SAML REST API v2 access enabled. Note that feature rollout across tenant environments is executed in a phased manner.
-
Service-Specific Usage Profiles – Administrators can assign specific usage profiles to SAML Forward Proxy IdP accounts, allowing decoupled authentication workflows across disparate Netskope access methods. Benefits include:
-
Applying strict security policies (such as mandatory step-up Multi-Factor Authentication) for sensitive Private Access applications.
-
Maintaining frictionless, single-sign-on access for general web browsing via Internet Security / Cloud Firewall.
-
Decoupling initial client enrollment policies from recurring re-authentication policies.
Usage Profile Description and Scope インターネットセキュリティ / クラウドファイアウォール / Private Access Governs client enrollment and initial authentication for Secure Web Gateway (SWG), Cloud Firewall (CFW), and Netskope Private Access (NPA). Borderless WAN Handles client enrollment and authentication flows for Netskope Borderless WAN endpoints. Private Accessの再認証 Applies to subsequent, step-up verification when users access sensitive NPA applications subject to re-authentication policies. Borderless WAN Re-Authentication Applies to subsequent verification for active Borderless WAN sessions requiring renewed credentials.
-
-
Standards-Compliant SAML ForceAuthn – Netskope now leverages the industry-standard SAML 2.0 ForceAuthn attribute, replacing the legacy browser cookie-clearing workaround. When enabled, Netskope includes ForceAuthn=”true” in the SAML AuthnRequest payload. This explicitly instructs the upstream Identity Provider to challenge the user for active credentials, regardless of any existing, valid SSO session at the IdP.
-
Interoperability: Natively supported by major enterprise IdPs including Microsoft Entra ID, Okta, and PingFederate.
-
Predictability: Eliminates inconsistent browser cache/cookie behavior during re-authentication cycles.
-
Security Compliance: Ensures step-up verification and MFA policies are reliably triggered for restricted resources.
-
-
Login Hint and Domain Hint Pre-population – To optimize user experience during mandatory re-authentication challenges, Netskope forwards identity context directly to the Identity Provider:
-
login_hint Parameter: Passed in authentication requests to supported IdPs (e.g., Okta, PingFederate) to pre-fill the username or email field.
-
domain_hint Parameter: Forwarded to Microsoft Entra ID SAML endpoints to bypass redundant tenant discovery and direct users immediately to their corporate sign-in page.
-
Certificate Extraction: The Netskope Client automatically extracts the user identity (email or User Principal Name) from the enrolled client certificate’s Subject field.
-
Supported Platforms: Available on Netskope Client for Windows and macOS during Private Access and Borderless WAN re-authentication workflows.
-
Netskope SAML設定を取得する
-
Netskope WebUIにログインしてください
-
Settings > Security Cloud Platformに移動し、[フォワードプロキシ] の下のSAMLをクリックします。
IdPでNetskopeアプリを設定する際は、 Netskope WebUIのSettings > Administration > SSOページからメタデータと証明書を取得します。 -
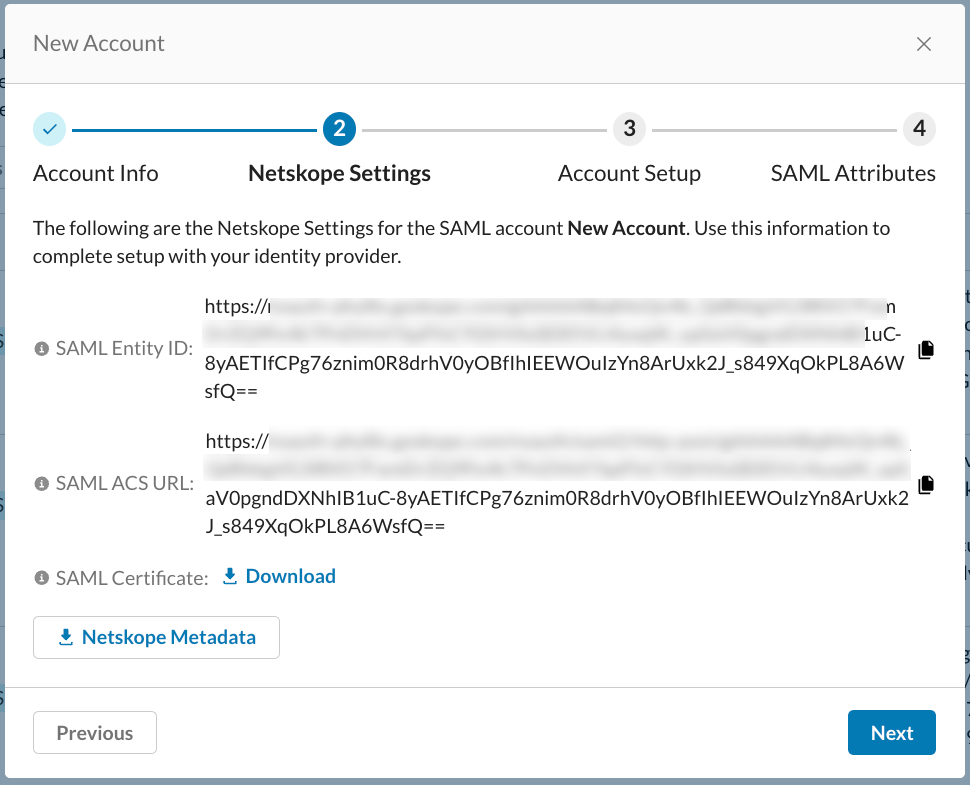
IdPアカウントが既に作成されている場合は、そのIdPアカウントでNetskope Settings をクリックし、以下をコピーしてください。
NetskopeでIdPアカウントを作成する方法の詳細については、 「新しいフォワードプロキシIdPサービスの追加」セクションを参照してください。-
SAML Entity ID
-
SAML Proxy ACS URL:
-
Download CERTIFICATE
-
新しいフォワードプロキシIdPサービスを追加する
新しい IdP を認証サービスとして追加するには、次の手順を実行します。
-
Go to Settings > Security Cloud Platform > SAML (in Forward Proxy).
-
Click the NEW ACCOUNT button. In the New Account pop-up window, configure:
-
Name: Provide a name to identify the IdP service.
-
Access Method: Select the access method that will use this IdP service
-
All – すべてのアクセス方法に対して IdP サービスを使用する。
-
IPSec – Select this option to use the IdP service for IPsec access methods. For granular control, you can enable the IdP service for all tunnels or specific tunnels.
-
GRE – To use the IdP service for GRE access methods. For granular control, you can enable the IdP service for all tunnels or specific tunnels.
-
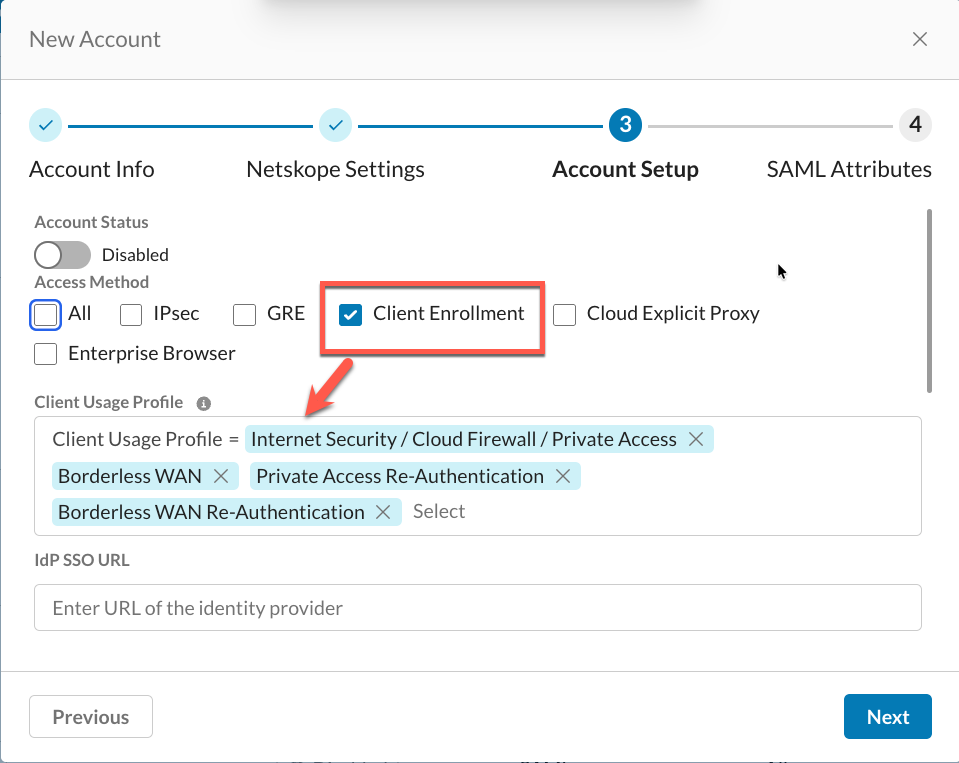
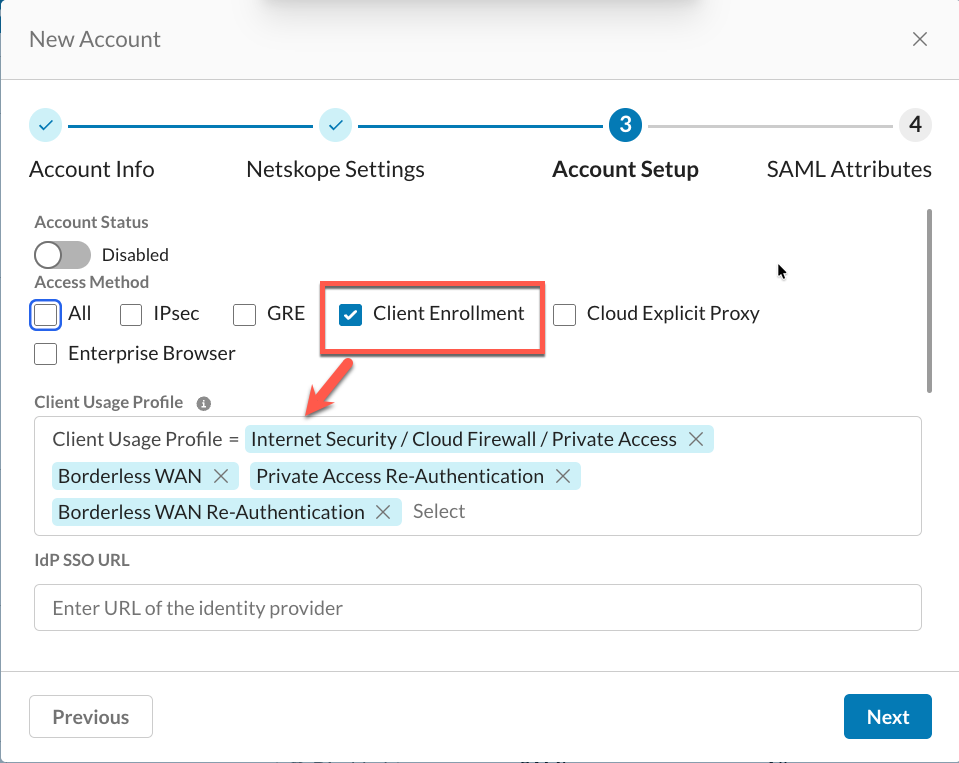
Client Enrollment – To use the IdP service for client enrollment and authentication workflows.
-
Cloud Explicit Proxy – アクセス方法がNetskopeプロキシ経由の場合のIdPサービス。
-
-
Usage Profiles (Applicable when Client Enrollment or All is selected): Select the service-specific profiles to assign to this IdP account. By default, all four profiles are selected:
-
Internet Security / Cloud Firewall / Private Access: Governs client enrollment and initial authentication for SWG, CFW, and NPA.
-
Borderless WAN: Handles client enrollment and initial authentication flows for Borderless WAN endpoints.
-
Private Access Re-Authentication: Applies to subsequent step-up verification when users access sensitive NPA applications subject to re-authentication policies.
-
Borderless WAN Re-Authentication: Applies to subsequent verification for active Borderless WAN sessions requiring renewed credentials.
At least one usage profile must remain selected when Client Enrollment is enabled. You cannot save an account with all profiles cleared. -
-
IdP Configuration: In the Setup tab, configure the IdP parameters:
-
IDP SSO URL: The URL used to redirect the user to the IdP site for authentication.
-
IDP Entity ID: A globally unique name for the SAML entity (IdP or SP).
-
IDP Certificate: Upload the X.509 certificate from the third-party IdP to validate the signature of the SAML assertion.
-
SAML Binding Method: Select between HTTP Post and HTTP Redirect.
-
Alternate User Id Field: By default, Netskope looks at the NameID field in the SAML assertion. If using another attribute, enter the SAML attribute name.
-
Select the Status toggle to enable or disable the IdP service.
-
-
-
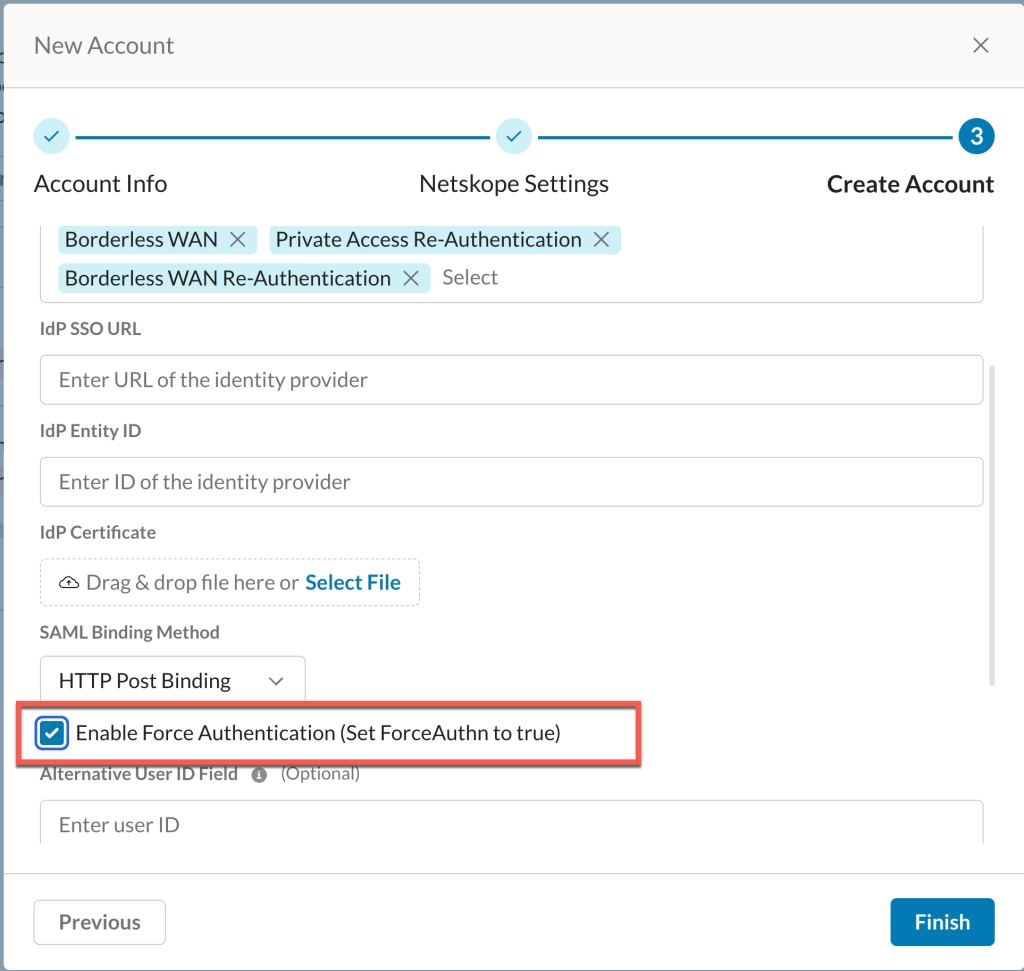
Options tab. (Force Authentication & Granular Controls). These are optional settings.
-
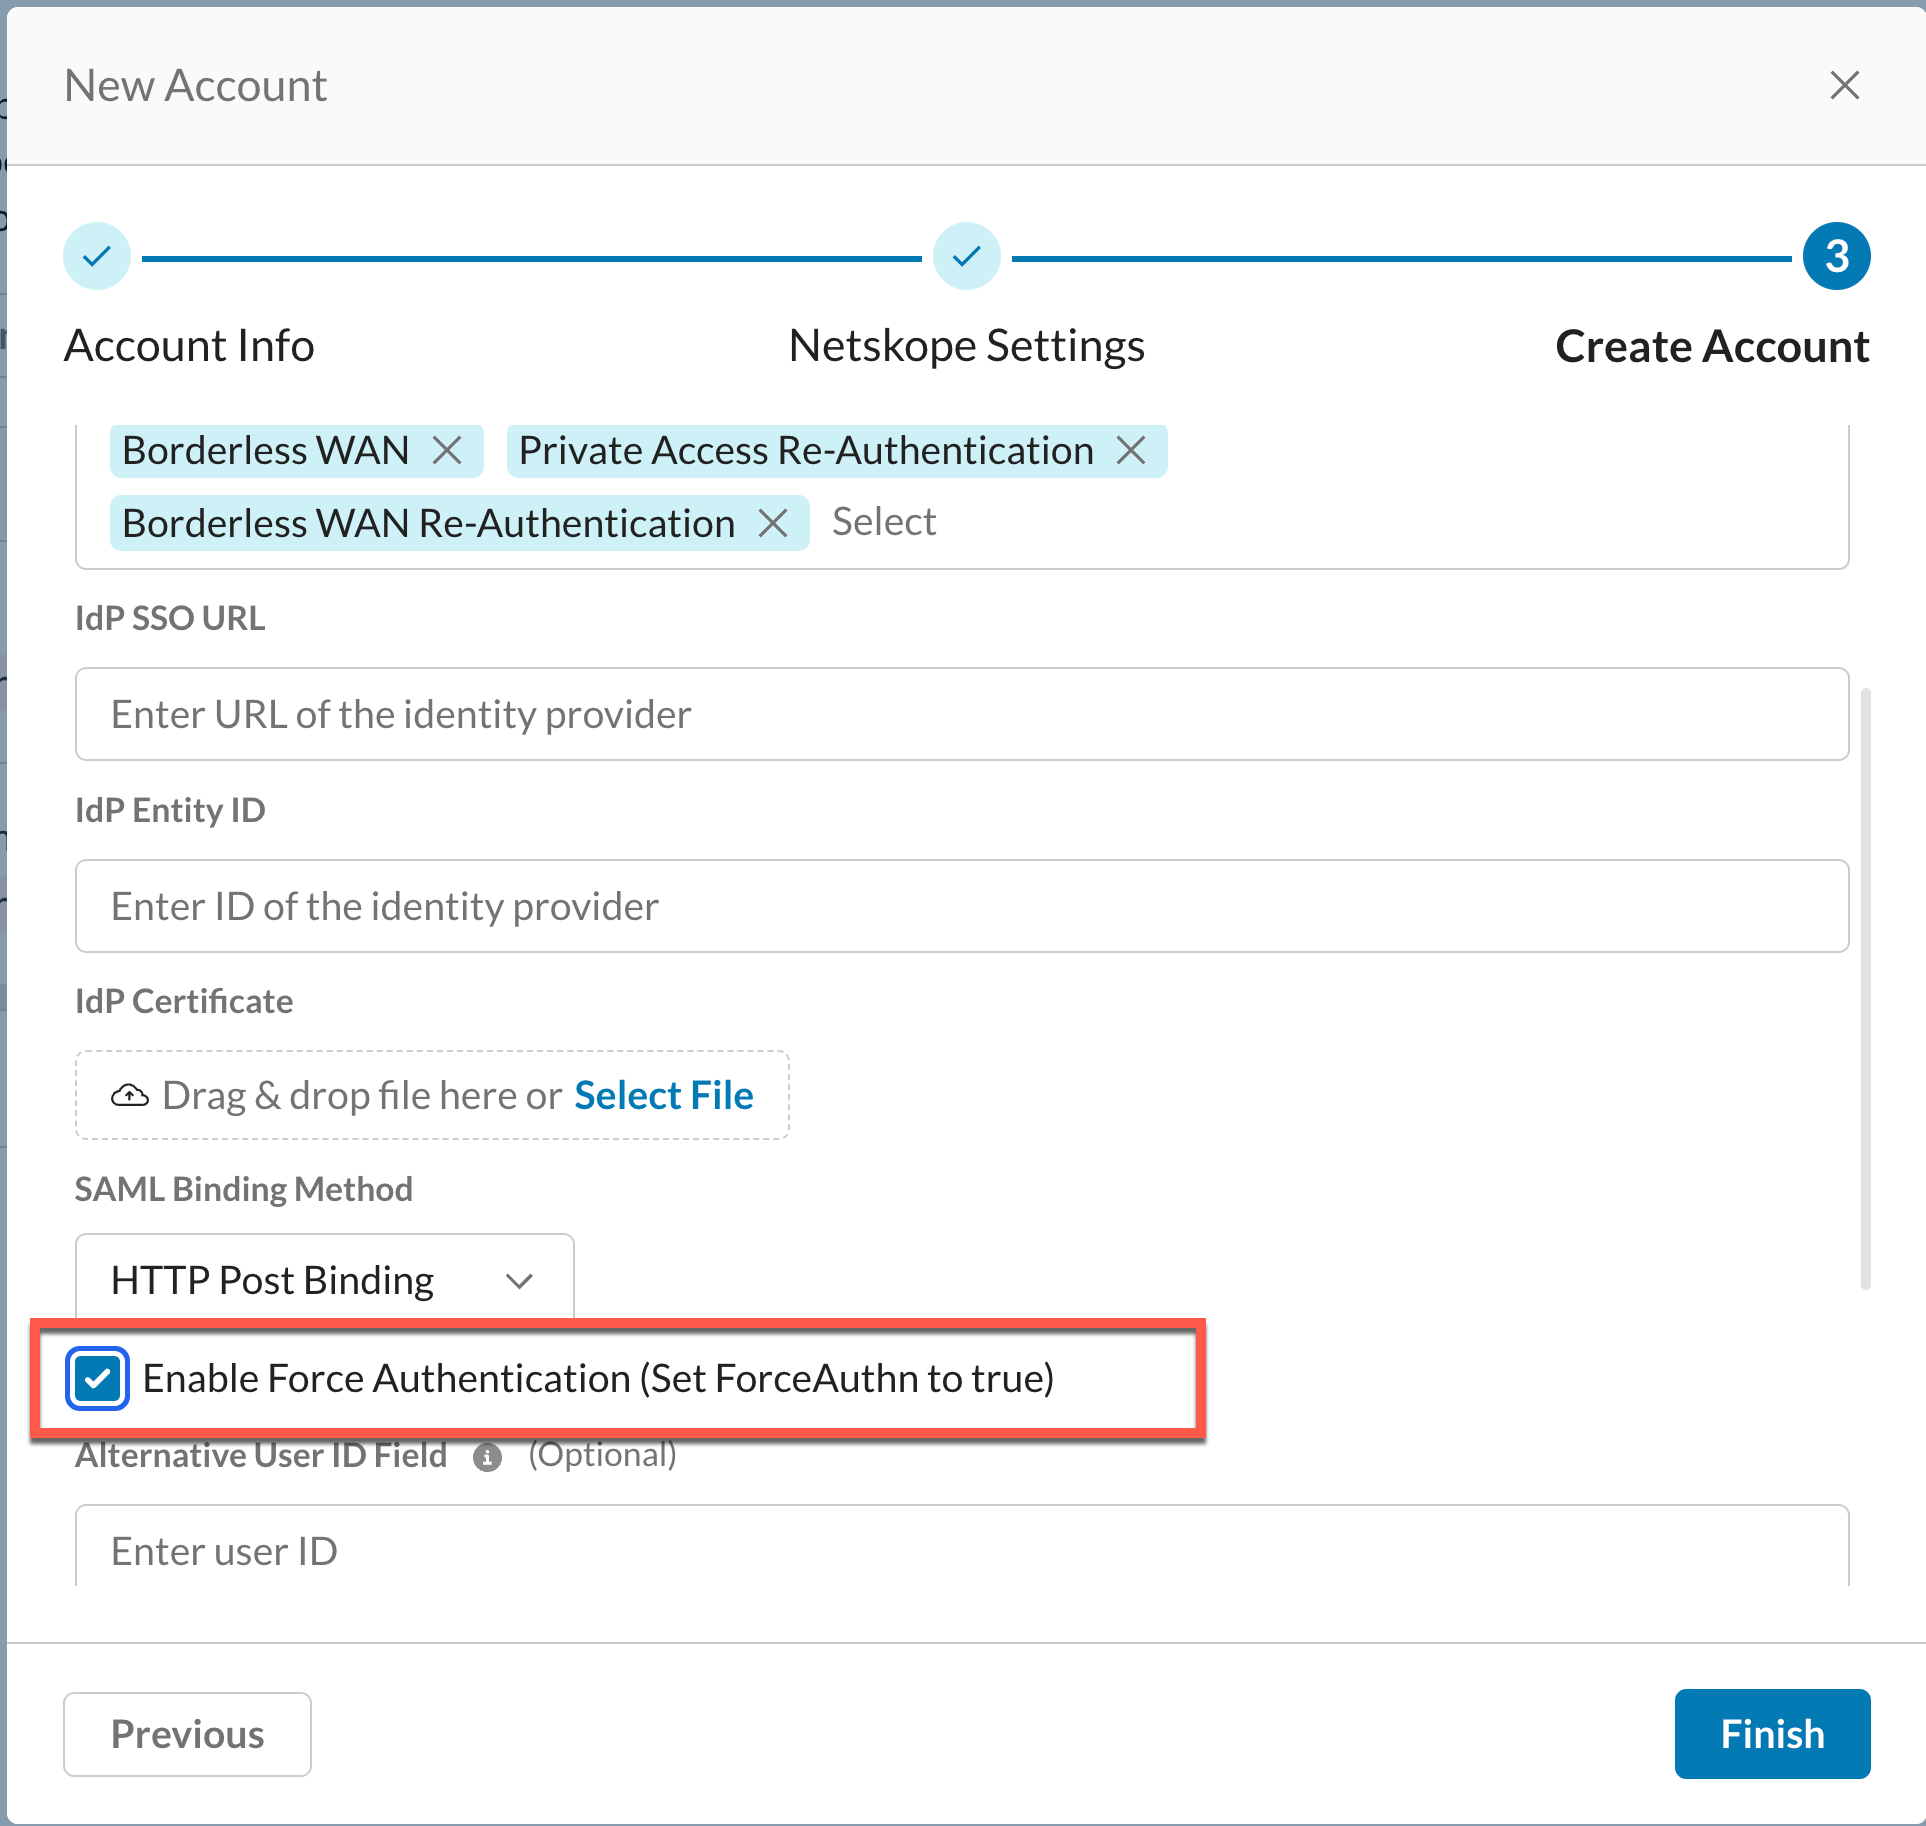
Force Authentication: Select to Enabled (ON). This instructs the IdP to challenge the user for active credentials again, even if an active SSO session already exists. When enabled, Netskope includes ForceAuthn=”true” in the SAML AuthnRequest payload. This replaces legacy browser cookie-clearing workarounds and ensures strict MFA compliance for re-authentication workflows.
-
Network Location & Domain Matching: Specify granular controls so the IdP is matched only when specific criteria (network location, authentication domain) are met.
-
-
SAVEをクリックしてください。
Example Deployment Configurations
Authentication requirements differ across customer environments and security postures. Administrators can configure multiple SAML IdP accounts to support tailored workflows:
-
Example Configuration A: General Client Enrollment and Browsing
-
Force Authentication: Unchecked (Disabled)
-
Assigned Client Usage Profiles: Internet Security / Cloud Firewall / Private Access, Borderless WAN
-
Workflow: Allows users to leverage active corporate SSO sessions for daily web access and initial tunnel connection without unnecessary sign-in prompts.
-
-
Example Configuration B: Dedicated High-Assurance Re-Authentication
-
Force Authentication: Checked (Enabled)
-
Assigned Client Usage Profiles: Private Access Re-Authentication, Borderless WAN Re-Authentication
-
Workflow: Enforces fresh credential entry and step-up MFA whenever access policies require re-authentication for protected internal services.
-
Adding a New Forward Proxy IdP Service with the REST API
SAML Forward Proxy IdP accounts can be created and managed programmatically using Netskope REST API v2 endpoints:
-
API Endpoint:
/api/v2/infrastructure/samlforwardproxyidpaccount(supportingGET,POST,PATCH, andDELETEmethods). -
Access Method & Profiles: In the REST API, client profiles are defined by extending the
accessMethodarray rather than using a separateusageProfileskey. Supported profile and access method values include:-
“ipsec-gateway”
-
“gre-gateway”
-
“client-enrollment”
-
“bwan”
-
“npa-reauth”
-
“bwan-reauth”
-
“enterprise-browser”
-
“Explicit”
-
“All”
-
-
Force Authentication Parameter: Pass
"enableForceAuthn": true(orfalse) in the payload to control SAML ForceAuthn behavior.
Forward Proxy Global Settings
管理者は このページからユーザー認証設定を構成できます。 Cookieサロゲートを有効にしたり、認証更新間隔を変更したり、ユーザー認証ドメイン更新間隔を変更したりできます。さらに、認証が不要な特定のドメインやウェブカテゴリをスキップすることも可能です。
IPサロゲートを使う
SAMLフォワードプロキシ認証では、IPサロゲートがデフォルトで有効になっています。Netskopeサービスは、ユーザーベースまたはグループベースのポリシー評価のために、ユーザーをプライベートIPアドレスにマッピングします。ユーザーとプライベートIPアドレスのマッピングは、設定された認証更新間隔に基づいて期限切れとなります。
クッキーサロゲートを使う
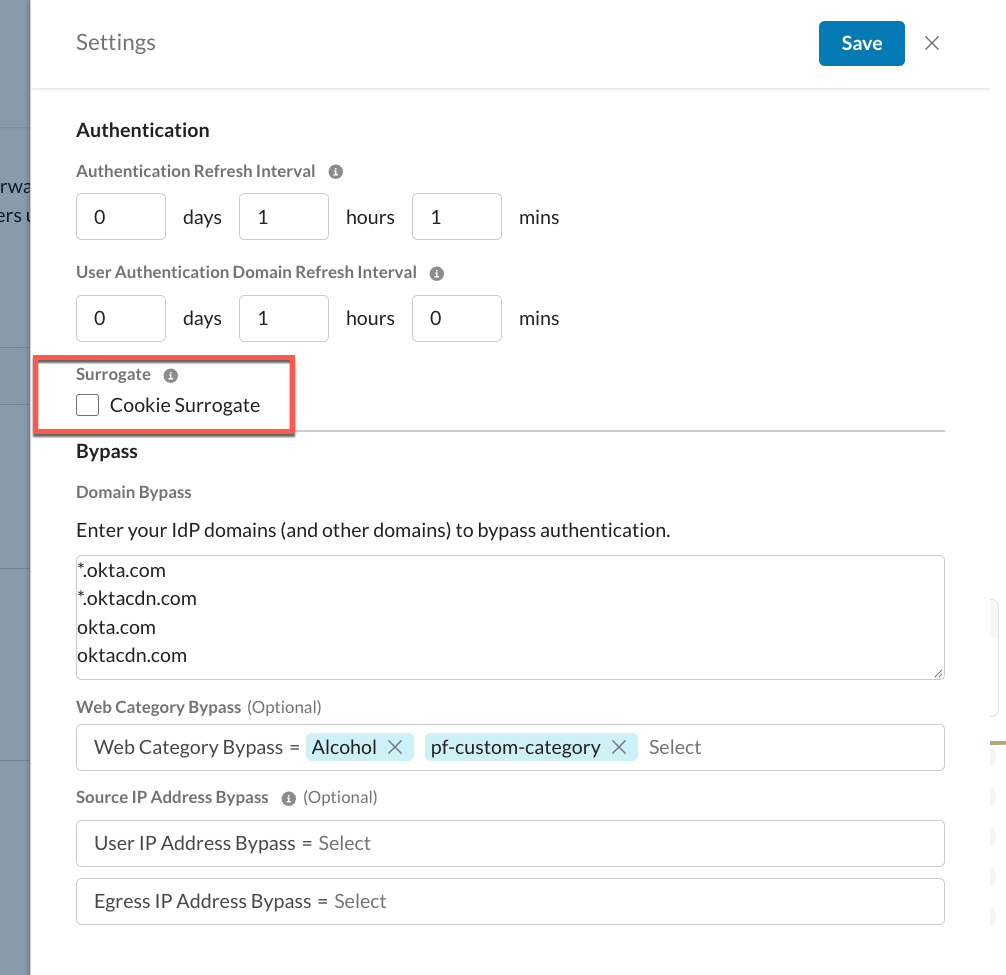
Cookieサロゲートは、ユーザーがNATの背後にいる場合に便利です。 Netskope Security Cloud Platform 、NATの背後にいるすべてのユーザーに対して同じIPアドレスを認識します。 この機能が有効になっている場合、Cookie サロゲートは、 ユーザー ID を取得するための Cookie を使用してこれを解決します。 この目的のために、NATのプライベートIPアドレスを入力してください。
To use a cookie surrogate, go to Settings > Security Cloud Platform > Forward Proxy > SAML and click Settings. In the Settings pop-up, select the Cookie Surrogate checkbox to enable, and then enter the source IP address (like 1.1.1.1) or subnet (like 1.1.1.0/24) for the cookie surrogate in the Source IP Addresses text field.
デスクトップアプリケーション用のCookie代替品
Cookie リダイレクトを尊重しないデスクトップ上のネイティブ アプリ、または Cookie を転送したりリダイレクトをサポートしたりするブラウザ ( .jsや.cssなど) からのバックグランド トラフィックでは、ユーザー ID が利用できない場合があります。 ユーザーIDが利用できない場合:
-
特定のアプリ、インスタンス、SSL復号化などへのアクセスに関するユーザー固有のポリシーは適用されません。
-
イベント(アプリケーション/ページ)にはユーザー情報は表示されませんが、ユーザーのIPアドレスは表示されます。
-
Cookieサロゲートを使用する場合、IdP認証はCookieに依存するため、ブラウザインスタンスごとに実行されます。
-
デバイス情報は、Cookieサロゲートではサポートされていません。
-
対策としては、問題のあるドメインに対する認証をバイパスすることなどが挙げられる。
IPSec/GRE Cookieサロゲートの制限事項
ウェブサイトの構造やクロスオリジンリソース共有(CORS)ポリシーによっては、nspatokenクッキーが省略されたり、リクエストの一部として送信できない場合があります。ユーザー認証の際、NetskopeはNetskopeサービスとユーザーのブラウザ間でnspatokenクッキーを設定および受信することにより、ユーザーの身元を確立します。ブラウザからの後続のリクエストにnspatokenが含まれていない場合、Netskopeは接続をブロックします。Netskopeは、ユーザーセッションの検証と通信の承認にトークンを必要とするためです。
更新間隔設定
SettingsポップアップのAuthenticationタブで、認証更新間隔とユーザー認証ドメイン更新間隔を設定できます。
認証更新間隔
このオプションは、IPサロゲートとCookieサロゲートトークンの両方に適用されます。認証トークンを一定期間後に更新するには、認証更新間隔の日数と時間を入力してください。デフォルト値は7日間、最小値は1時間、最大値は180日間です。
IPSec、GRE、またはEPoTの展開では、エンドデバイスから次のPOSTリクエストを実行することで、トンネルの背後にあるIPサロゲートの特定のユーザーとIPのマッピングを強制的に期限切れにすることができます。
curl -X POST -H "X-NS-REMOVE-AUTH-ENTRY: 1" -H "Content-Type: application/json" -d "{"comment": "<enter your comment>"}" https://nsauth-<enter your tenant>.goskope.com/
インラインユーザーのIPサロゲートが削除されると、監査イベントが生成されます。このアクティビティは、curlコマンド内で「認証エントリを削除しました」という名前と、それに続くあなたのコメントとして表示されます。監査イベントを表示するには、 Settings > Administration > Audit Logsに移動してください。
ユーザー認証ドメインの更新間隔
IdP選択用のユーザー認証ドメインを設定すると、ユーザーにIDの入力を求める頻度を制御できます。 ユーザー認証ドメインの更新間隔(日数と時間)を入力してください。この機能はオプションです。デフォルト値は7日間、最小値は1時間、最大値は180日間です。
バイパス設定
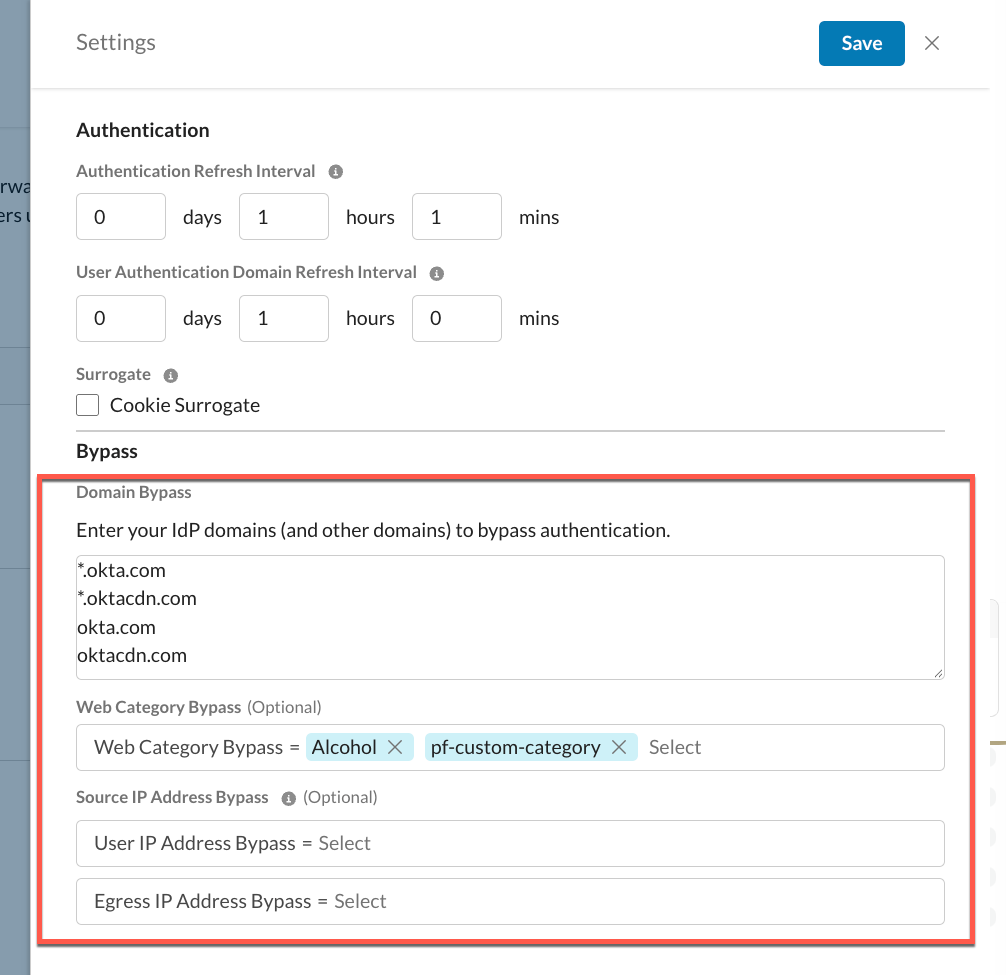
You can specify domains, web categories, and network IP addresses for which user authentication is not required. To specify authentication bypass settings, go to Settings > Security Cloud Platform > Forward Proxy > SAML and click Settings.
ドメインバイパス
クリックして、カンマ区切りのURLを追加し、バイパスしてください。完了したら、 Saveをクリックしてください。
ウェブカテゴリバイパス
クリックして、バイパスするURLをカンマ区切りで追加します。完了したら、 Saveをクリックしてください。
送信元IPアドレスバイパス
クリックしてソースネットワークを編集および検索します。検出された各ネットワークについて、ユーザーIPアドレスまたは送信元IPアドレスのいずれかに基づいてバイパスするかどうかを選択できます(両方ではなく、どちらか一方のみ)。テキストフィールドにIPアドレス、IPアドレス範囲、またはCIDRネットマスクを入力してください。クリック 複数のネットワーク拠点を追加するためのアイコン。ネットワークの場所を追加したら、 Saveをクリックします。