

Use a DLP profile to define the sensitive content to inspect and the action to take when that profile matches. The following page contains the full private-app DLP procedure and limitations.
Before You Begin
- Enable the required NPA DLP entitlement.
- Configure a matching application access policy.
Configure Data Loss Prevention Policies
Netskope Private Access supports applying Data Loss Prevention (DLP) to private apps by using Private App Access real-time policies. Use this configuration to inspect and protect sensitive data for both Browser Access and Client access to private apps. For Browser Access, you can also scope the policy to specific browser activities. For information about creating DLP profiles, rules, and identifiers, see Data Loss Prevention.
Prerequisites
- Ensure a Publisher is already configured.
- For Browser Access, confirm a SAML reverse proxy IdP for Private Apps is configured.
- For Browser Access, verify the private app is configured for Browser Access.
- Create the DLP profile you want to apply before creating the policy
Configure a DLP policy for Private Apps
- Go to Policies > Real-time Protection and create or edit a Private App Access policy. The broader real-time policy framework supports DLP and Threat Protection and includes Private App Segment Access as a policy type.
- For Source, select the users or groups to which the policy applies, and set the Access Method to Browser Access, Client, or both, depending on the use case.
- For Destination, select the Private App Segment(s). Ensure the specific Activities are configured in order to be able to define a Data Loss Prevention Profile.
- For Profile & Action, select Add Profile and choose the required DLP Profile(s).
- Choose the enforcement action, name the policy, and click Save.
- This DLP Policy only inspects traffic; it does not grant access to the private app. Create a separate Private App Access Policy with an Allow action for the same app and users, and place it after this DLP rule in your policy order so the DLP profile is applied. (From R142 this order is no longer important.)
Additional Notes
- For NPA Browser Access DLP, only HTTP and HTTPS private apps are supported. AnyApp Browser Access apps such as RDP/SSH are not supported for DLP.
- For NPA Client Access DLP, only HTTP and HTTPS over port 80 and 443 are supported.
- Transaction events are not generated for DLP traffic, even when transaction events are enabled for web traffic.
- Review the Supported File Types for Content Inspection for file-format coverage.
- OCR is an Advanced DLP capability in Netskope generally, but OCR is not supported for NPA.
Validation
After saving the policy, test access to the private app with representative content that should trigger the selected DLP profile. Confirm the expected enforcement result and review the resulting DLP alerts or incidents.
Related links
- Enforce DLP for NPA Browser Access Private Apps for Browser Access-specific prerequisites and legacy context.
- Data Loss Prevention / About DLP for profiles, rules, identifiers, and incidents.
- Supported File Types for Content Inspection for file-format coverage.
Profile Actions and Editor Behavior
The editor provides Alert, Allow, and Block for the DLP inspection configuration. Choose Block when matching sensitive content must not be transferred, and select the required notification template. If different profiles require different actions, select Set action for each profile and configure each displayed profile action.
If Activities is inactive before a profile is added, select Add Profile > DLP Profile, accept the activity-required confirmation, and then select the required activities. Before saving, verify that the selected activities and profile together match the intended inspection scope.
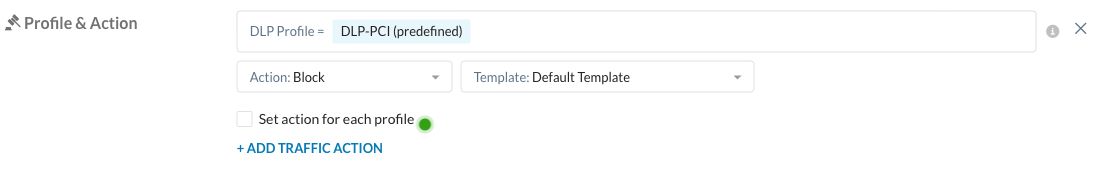
The Allow action within an inspection configuration does not replace the application access policy required in R142. After saving, review the applicable policy ordering and click Apply Changes.
DLP Limitations
- Client inspection supports HTTP and HTTPS traffic on ports 80 and 443.
- Browser Access DLP supports HTTP and HTTPS private applications. RDP and SSH AnyApp Browser Access sessions are not supported for DLP.
- Private app tags are not supported for Browser Access DLP in the documented scope; select individual segments.
- NPA does not support OCR inspection in this documented workflow.
- Transaction events are not generated for NPA DLP traffic, even if they are enabled for web traffic.
- File-format support, file-size limits, activity detection, and Browser Access-specific exceptions still apply. See Supported File Types for Content Inspection and Enforce DLP for NPA Browser Access Private Apps.
For DLP profile, rule, identifier, and incident configuration, see Data Loss Prevention.
Validate Inspection
In addition to the validation above, follow the inspection validation checklist. Test matching and nonmatching content for the configured activity and file constraints.