

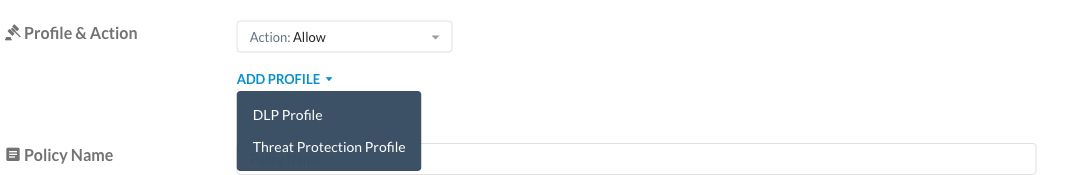
Use Profile & Action to configure access decisions and content inspection for private applications. An access action controls whether a user can connect. An inspection profile identifies the content or threats to detect and the action to take when inspection matches.
For the complete policy workflow, see Private App Segment Policy Management.
Profile and Action Documentation
| Page | Use it to |
|---|---|
| Access Actions | Configure Allow, Block, and authentication-based access decisions. |
| Data Loss Prevention Profiles | Configure DLP inspection, profile actions, activities, and content validation. |
| Threat Protection Profiles | Configure malware inspection, severity actions, hash lists, and patient zero behavior. |
| Per-App Periodic Authentication | Configure authentication intervals and understand the shared authentication timer. |
Inspection Profiles
| Profile | Purpose | Access-method coverage |
|---|---|---|
| Data Loss Prevention (DLP) Profile | Detects sensitive content according to the selected DLP rules and profile. | Client and Browser Access, within the supported HTTP/HTTPS scope. |
| Threat Protection Profile | Scans supported private web traffic for malware and other licensed threat detections. | Client access. |
The tenant must be entitled to the inspection capabilities being configured. A profile does not enable an unlicensed inspection engine.
Access and Inspection in R142
For each protected application, configure:
- An access policy for the intended users, access method, and private app segments, with Allow or the appropriate supported authentication action.
- A separate DLP or Threat Protection policy for the inspection required on those applications.
On releases before R142, place the inspection policy above the access policy. In R142, that relative ordering is no longer required to combine access and inspection. This change does not remove the need to review the order of competing access rules.
Before upgrading to R142, review applications that currently rely on an inspection policy to provide access. Add the matching access policy before the upgrade to avoid loss of connectivity. If the tenant is not entitled to the configured NPA inspection capability, remove the unsupported inspection policy as part of the policy review.
Validate Inspection
- Verify that an authorized user can reach the application through the intended access method.
- Use an approved, harmless test file or test content to trigger the selected profile.
- Test the configured activity and file constraints. Confirm the expected block or alert result.
- Test content that should not trigger the profile.
- Review the applicable alerts and, for DLP, incidents. Confirm the user, application, activity, profile, and enforcement result.
If access works but inspection does not, check the profile entitlement, selected application and activities, file constraints, traffic protocol and port, access method, and policy ordering for your release.
When an inspection service uses a fallback action, the resulting event can differ from a normal profile-match event. For example, some fallback events can lack a policy name. Review the inspection or fallback reason rather than assuming that an absent policy name proves no enforcement occurred.